Test your Microsoft 365 security, every day, in one run.
Maester
PS>Install-Module Maester -AllowPrereleaseInstall-Module MaesterInstalls the 3.0 preview, which these docs describe. About the previewInstalls the stable release, 2.3.0. 2.x docs
Runs on Windows, macOS and Linux · Nothing leaves your tenant
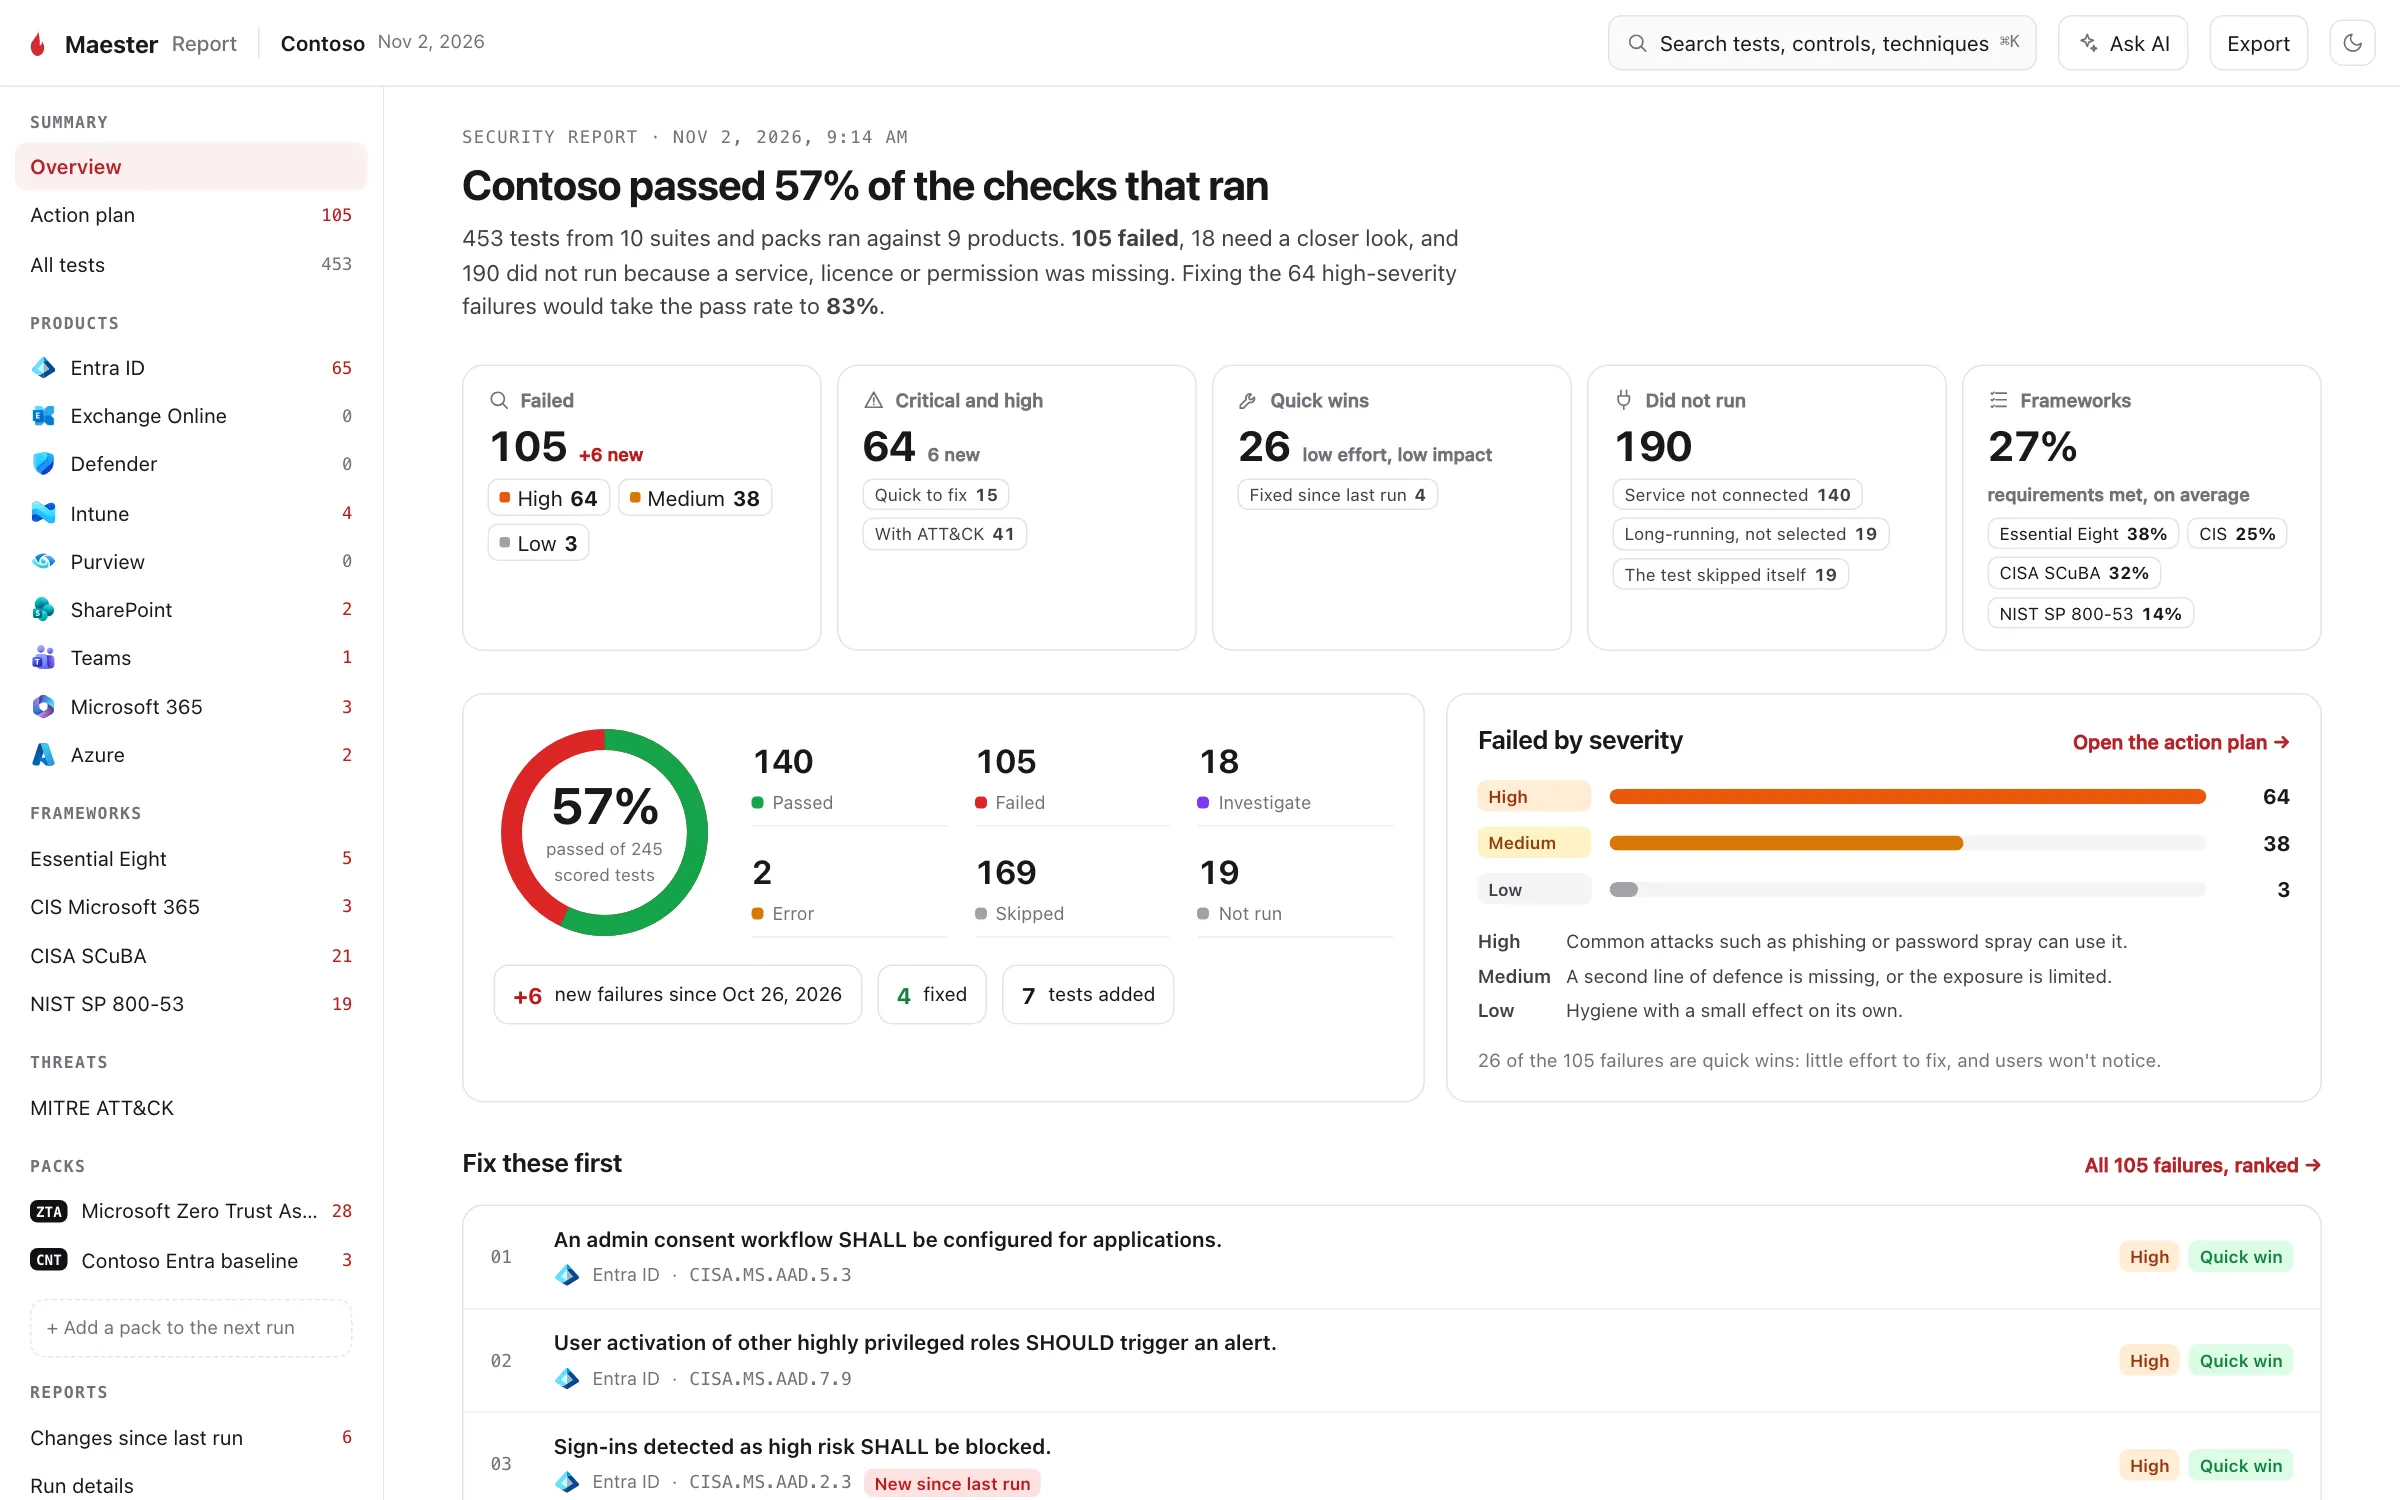
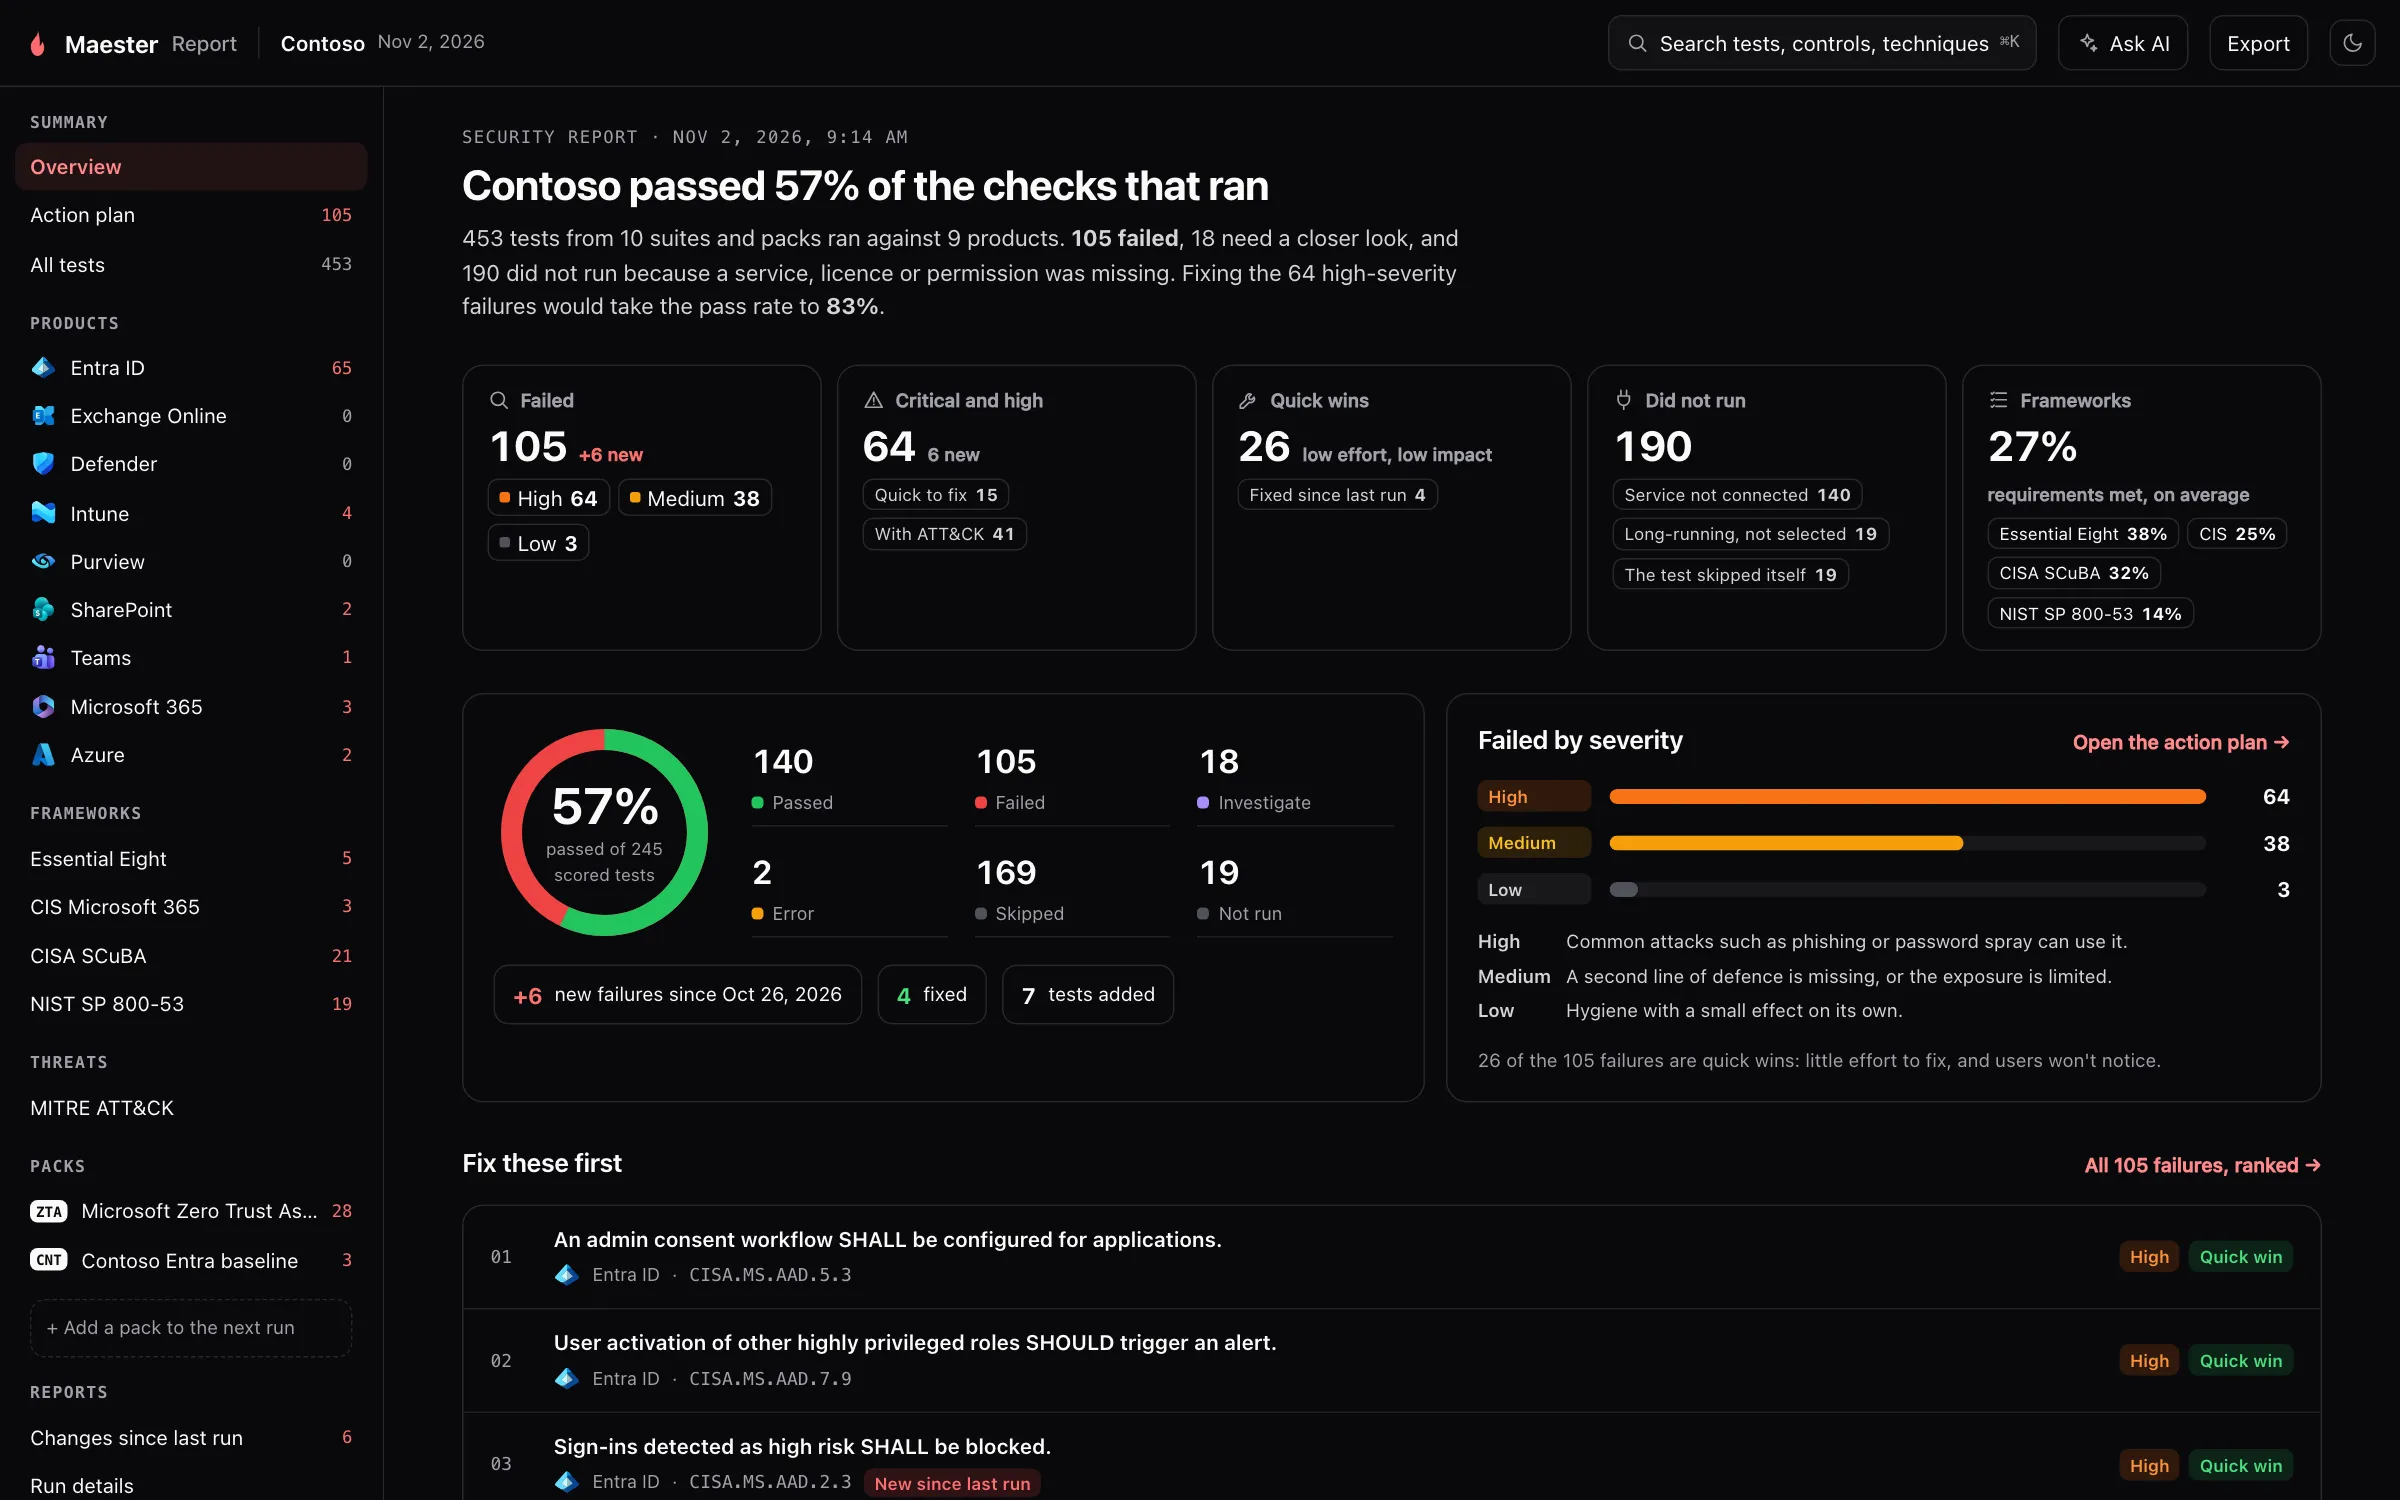
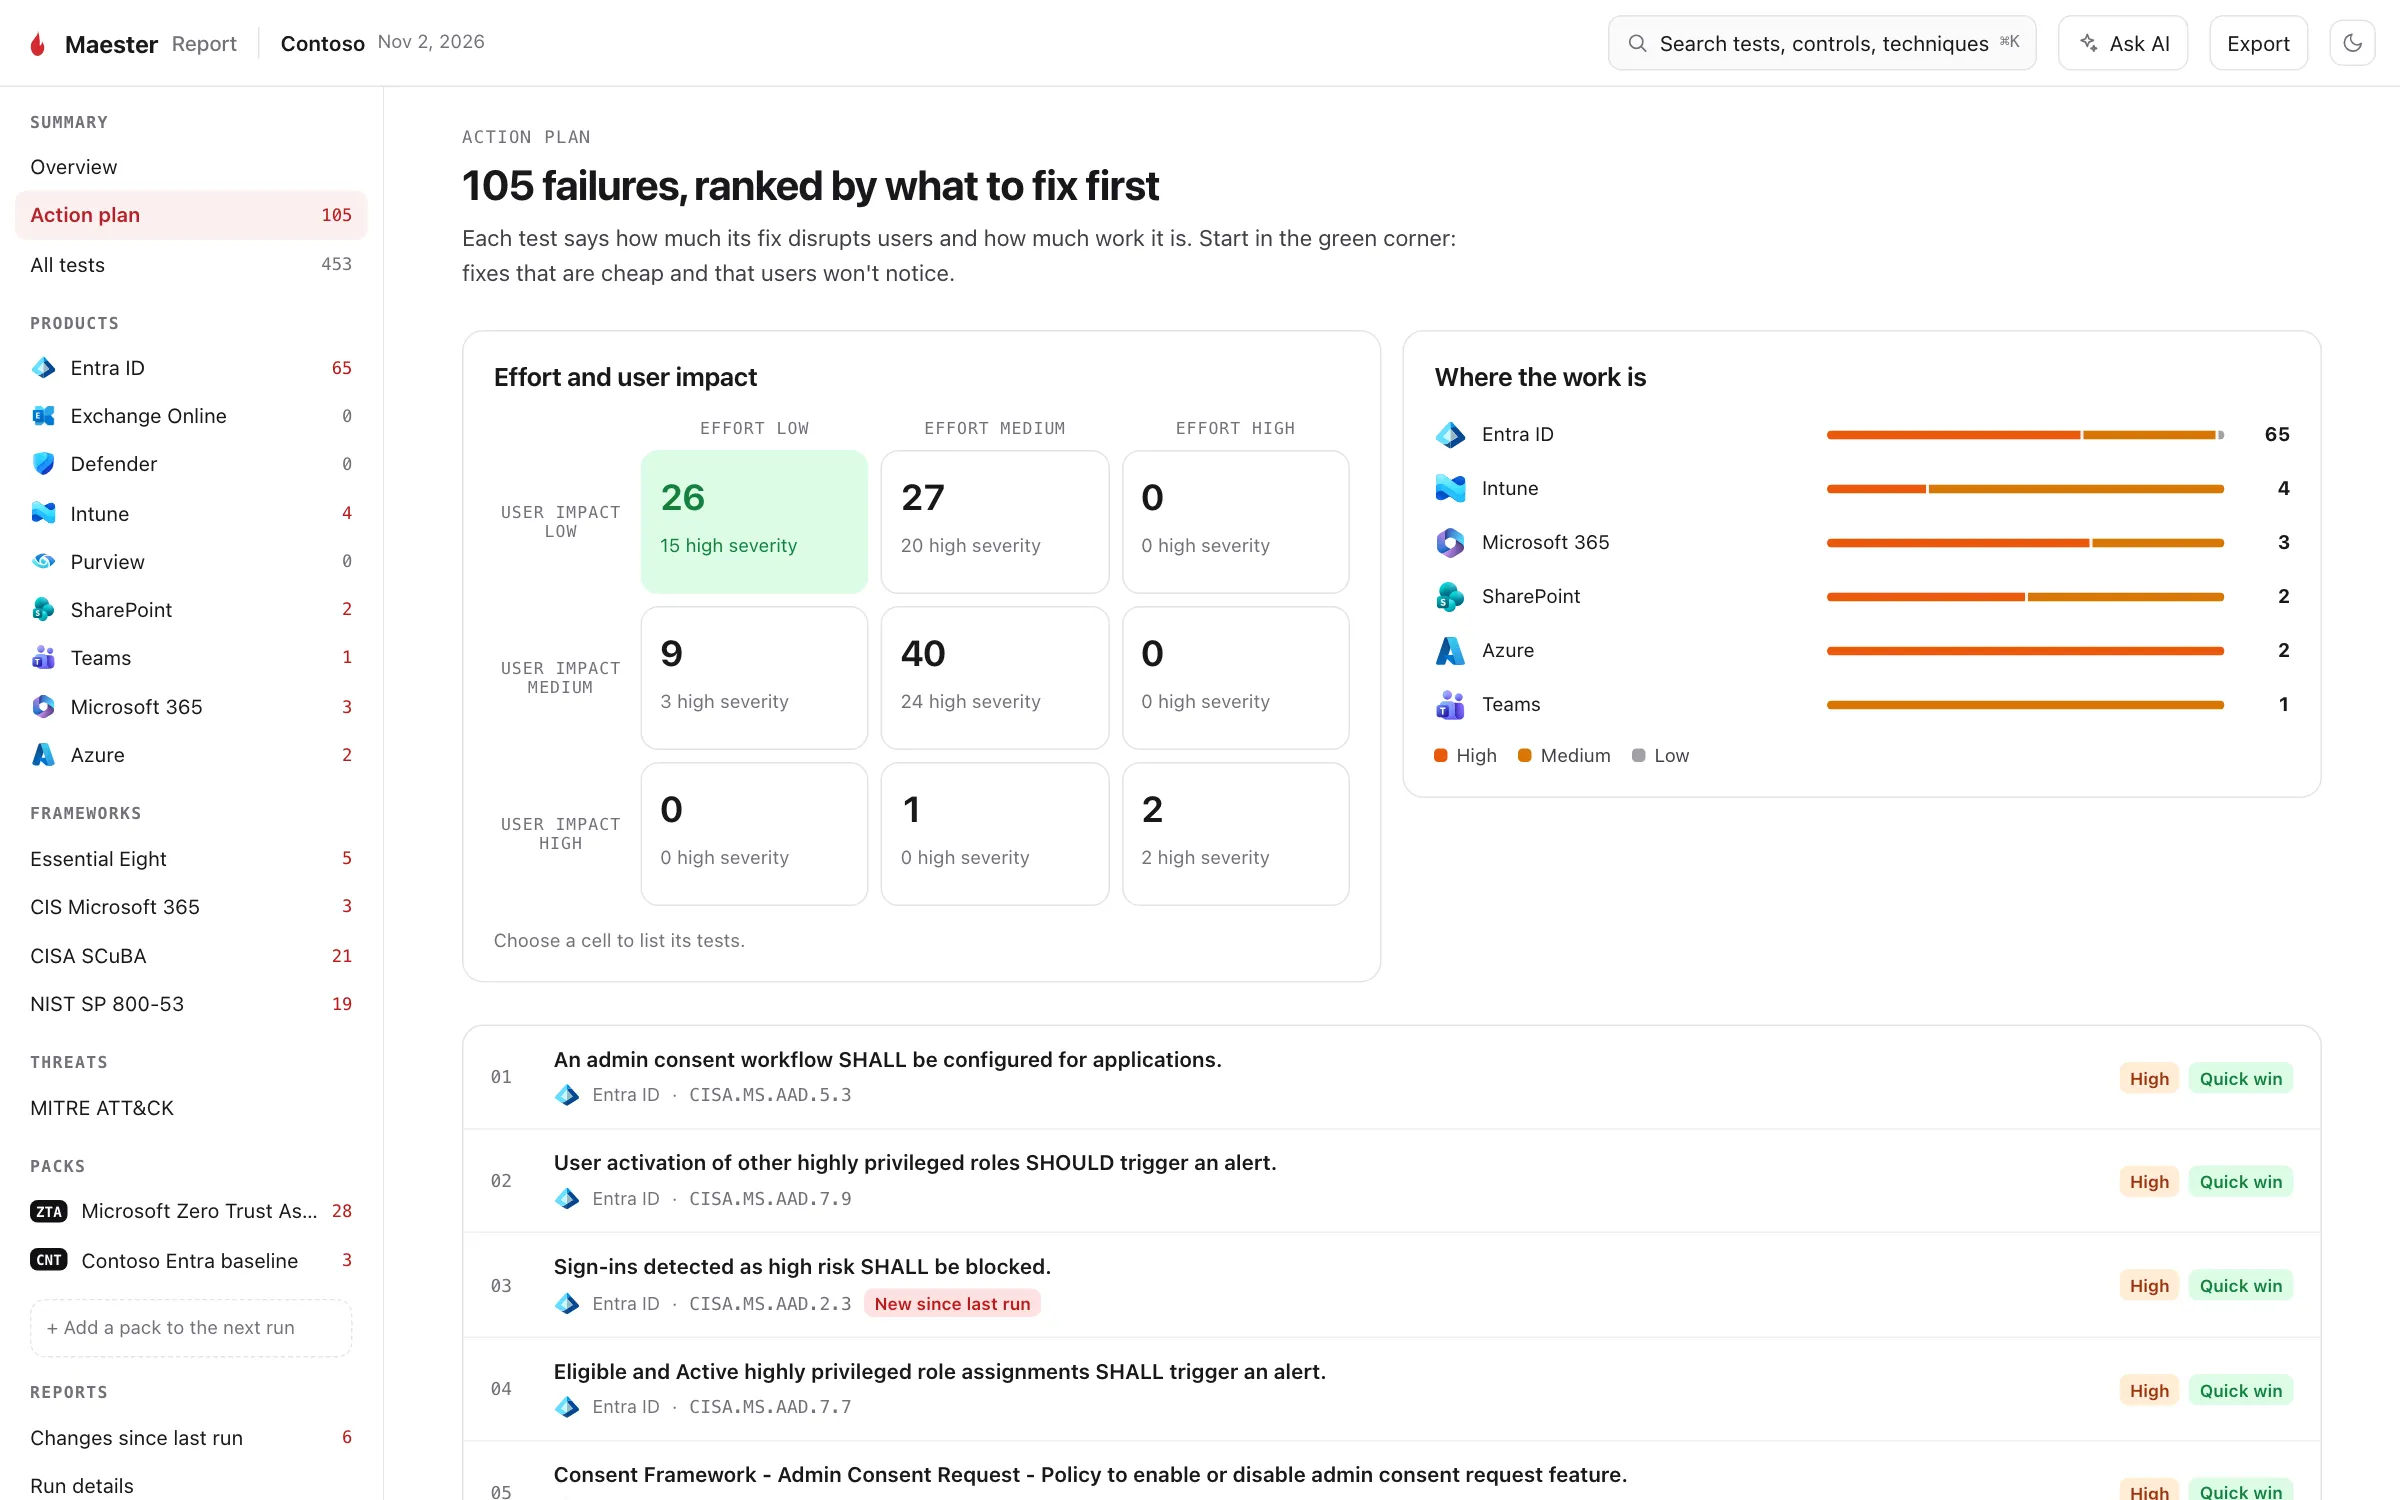
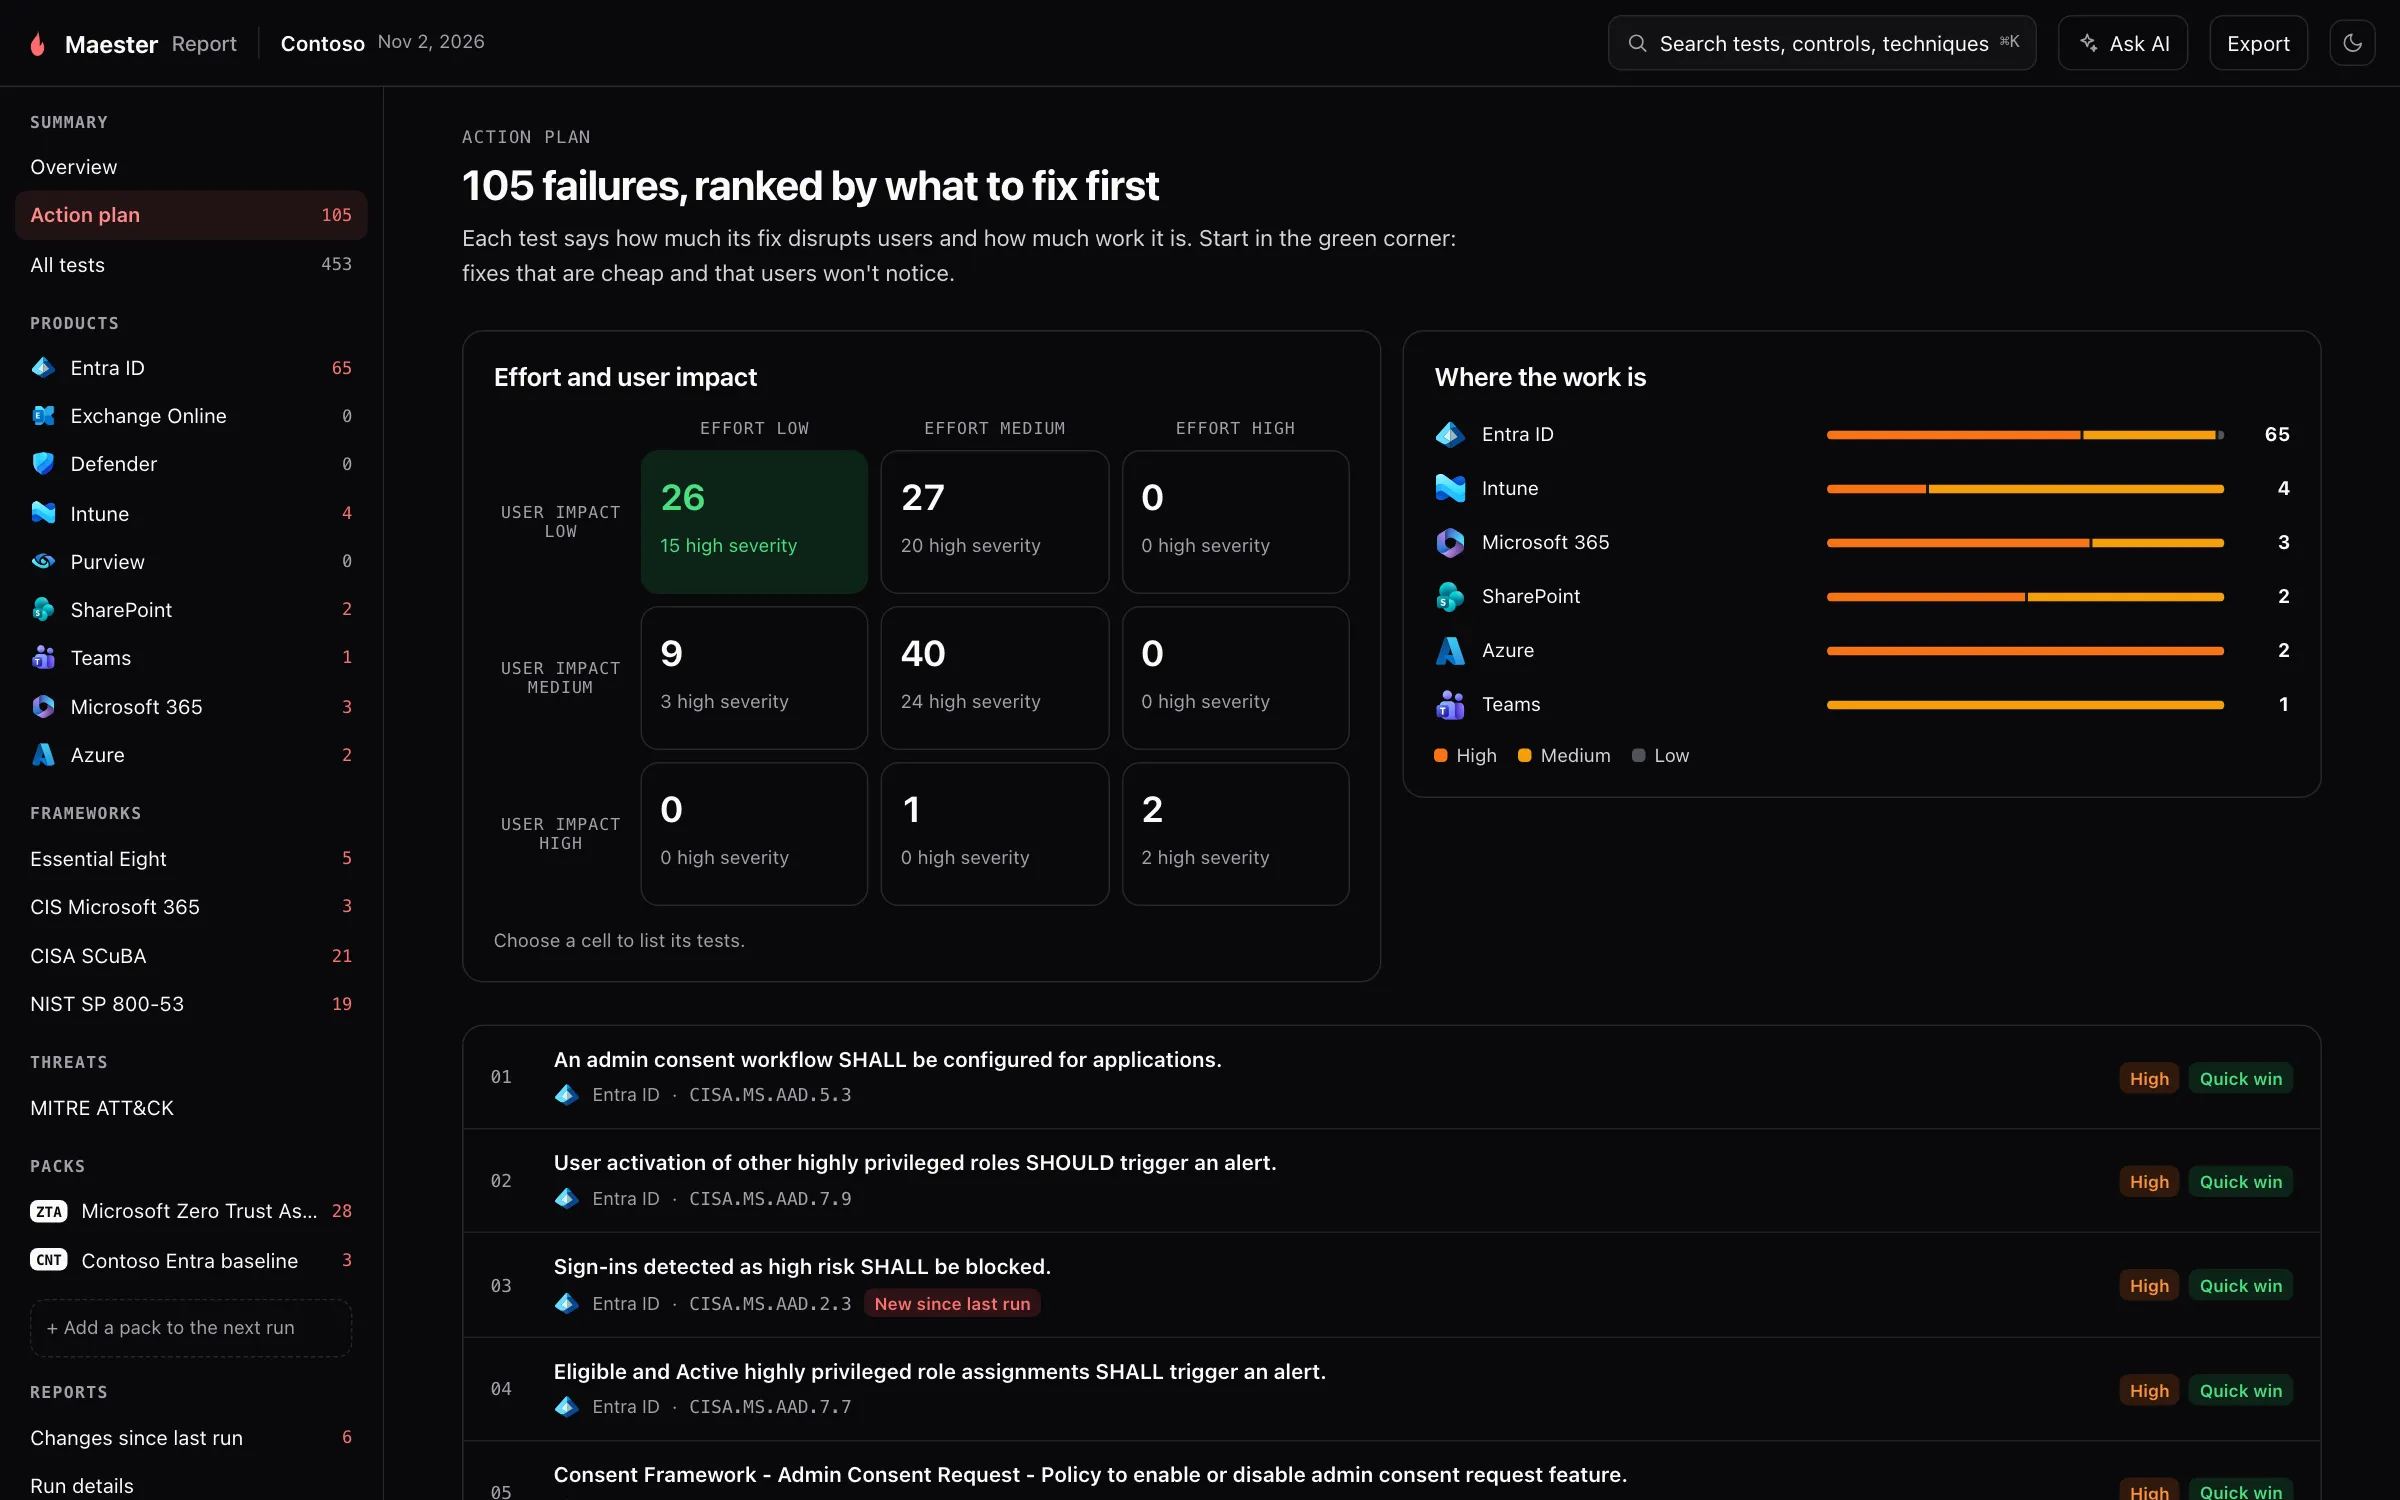
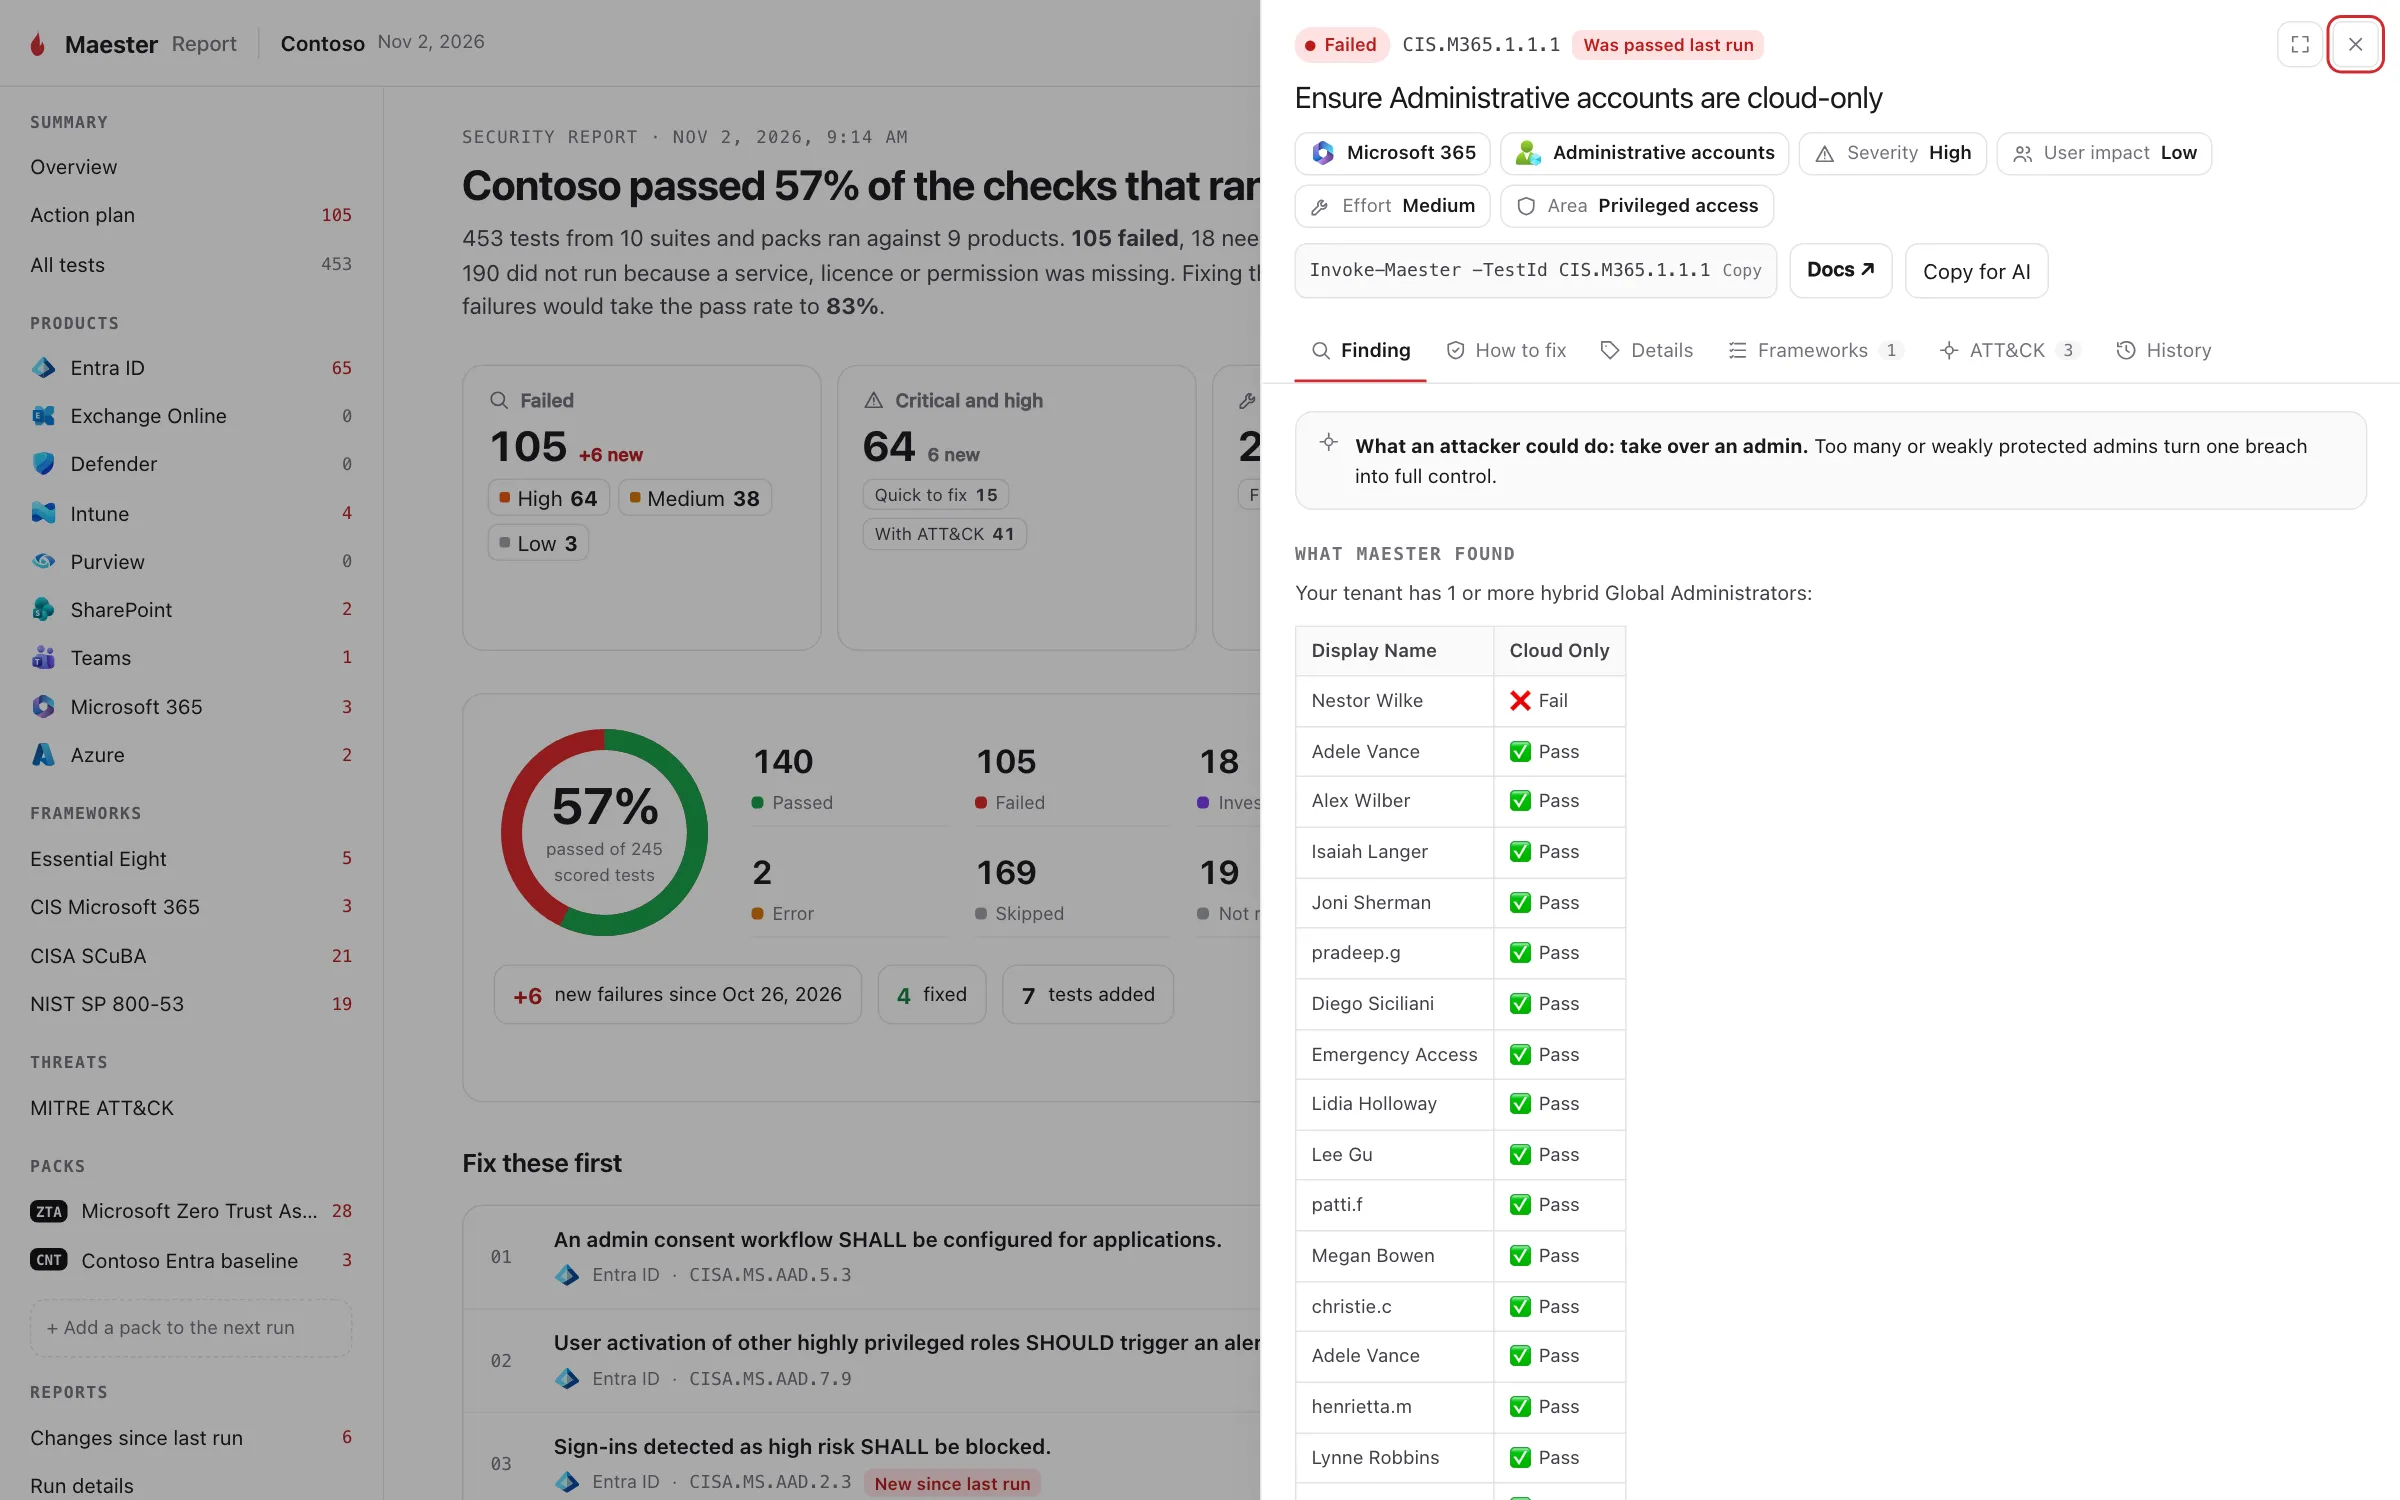
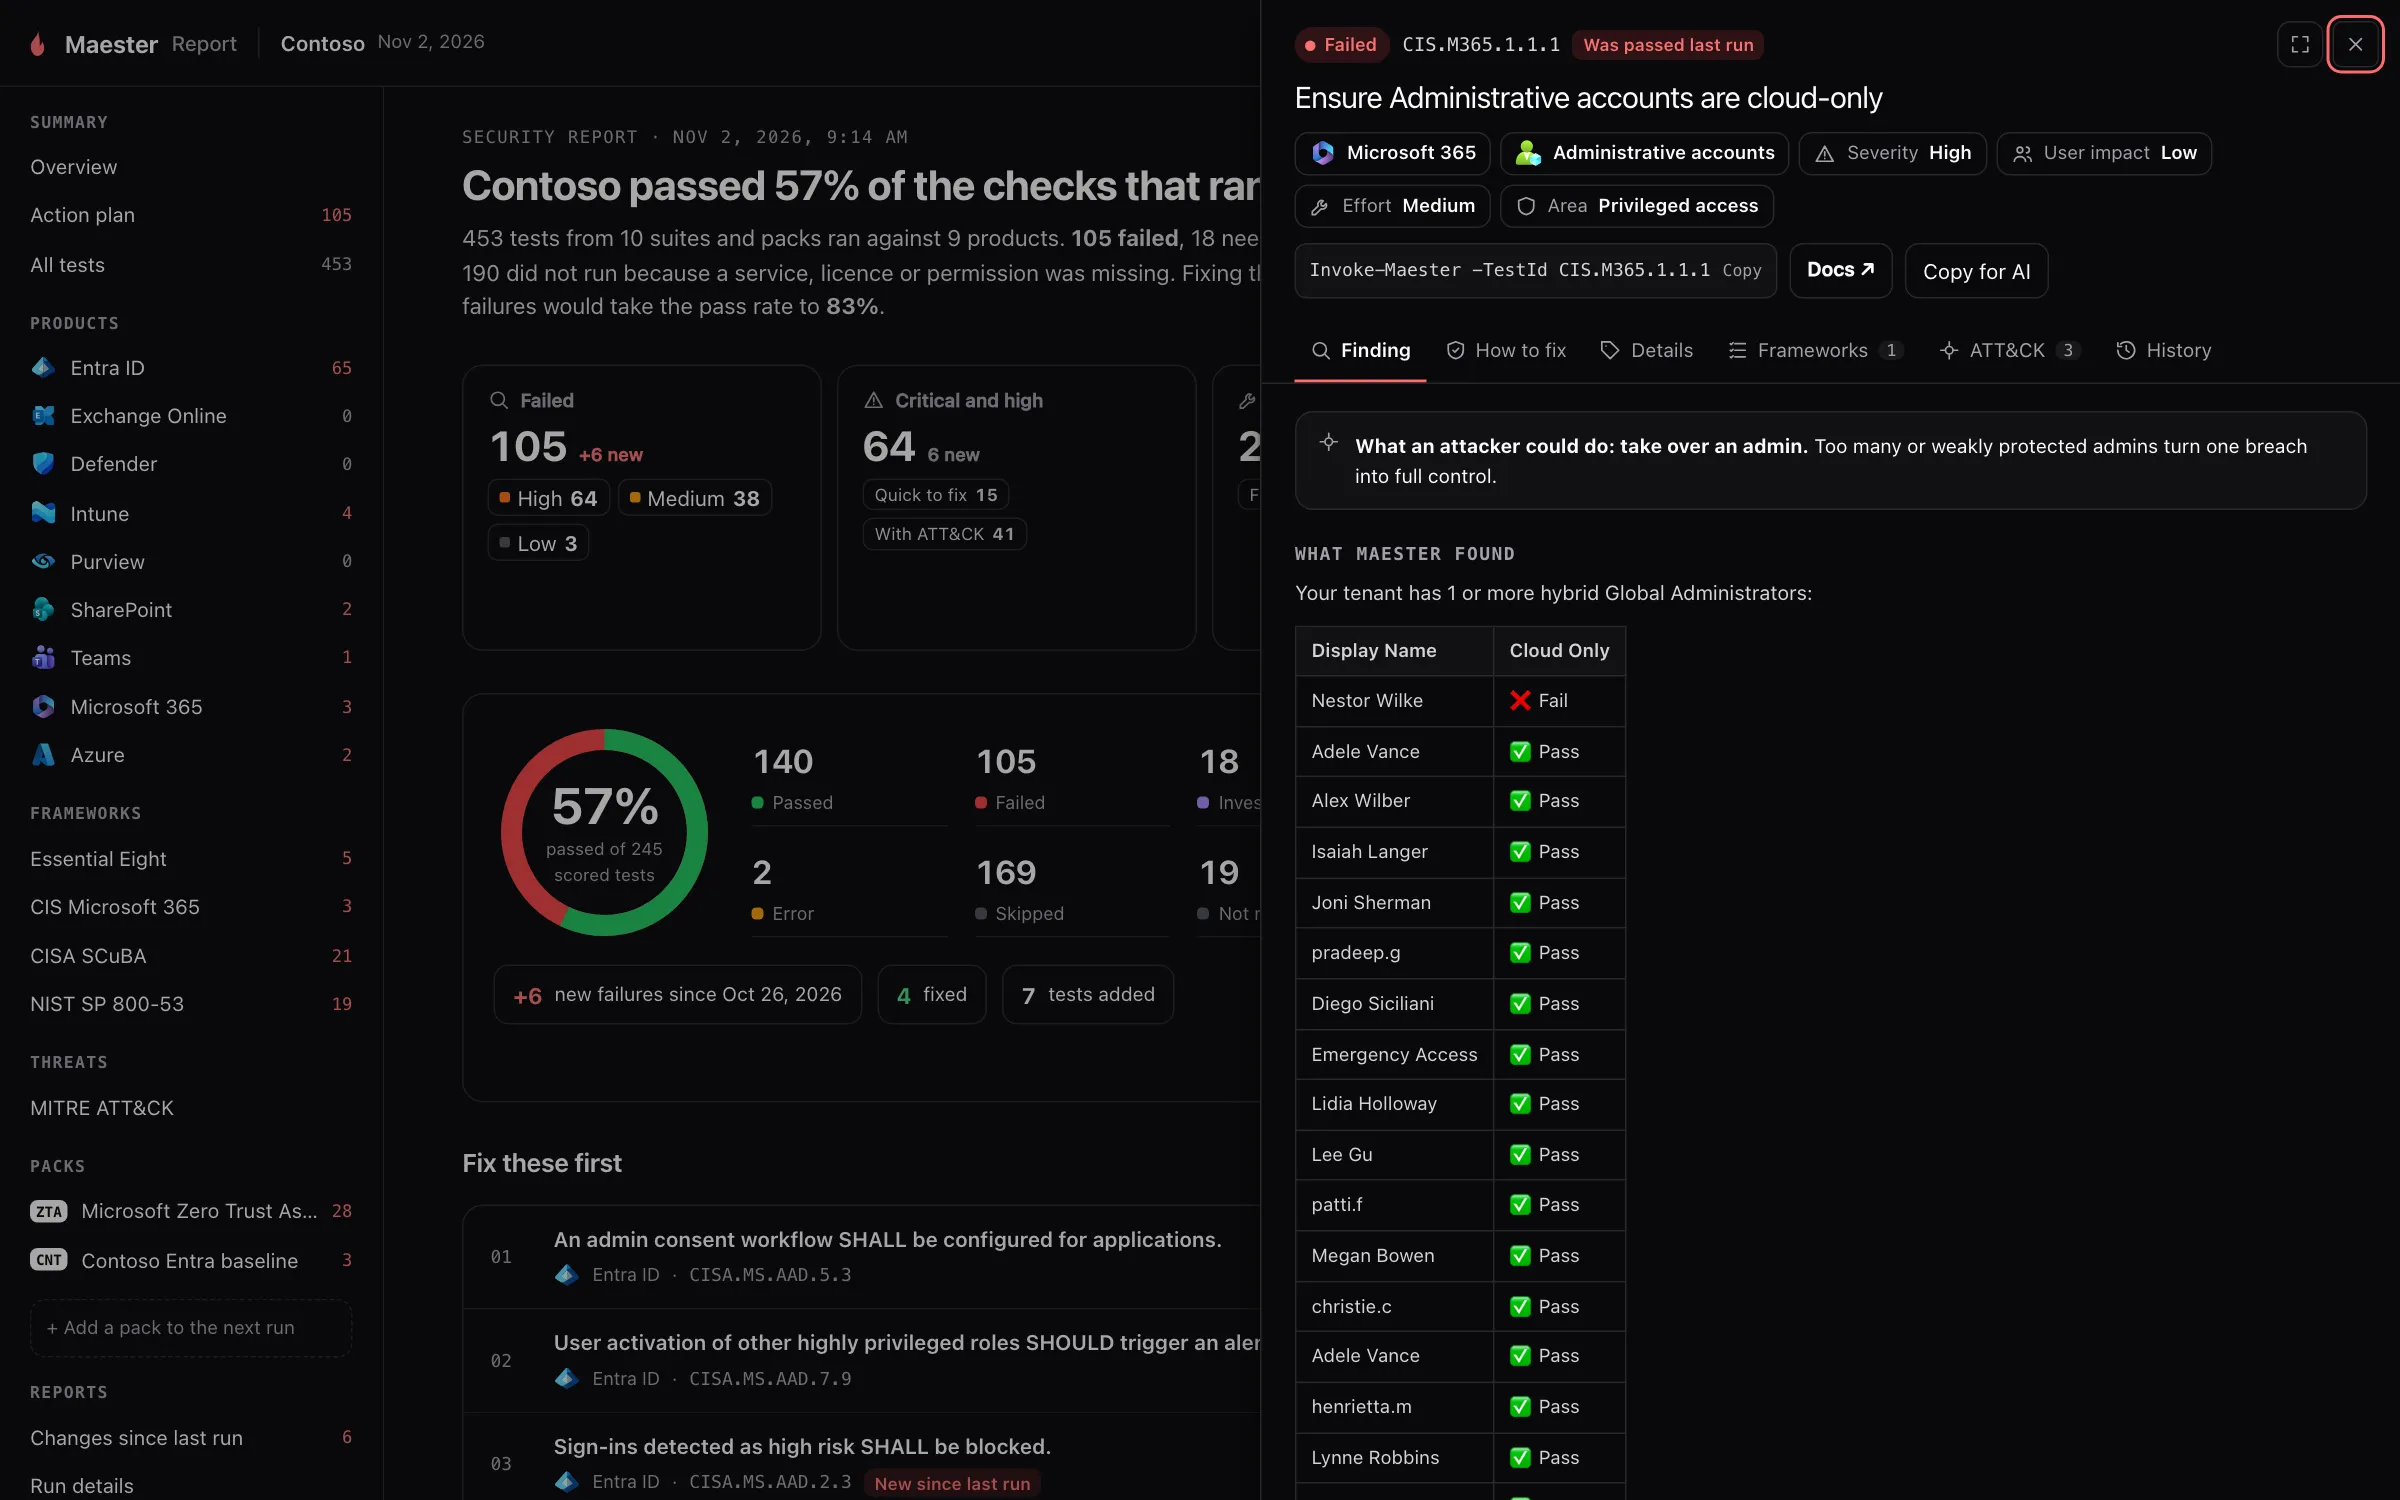
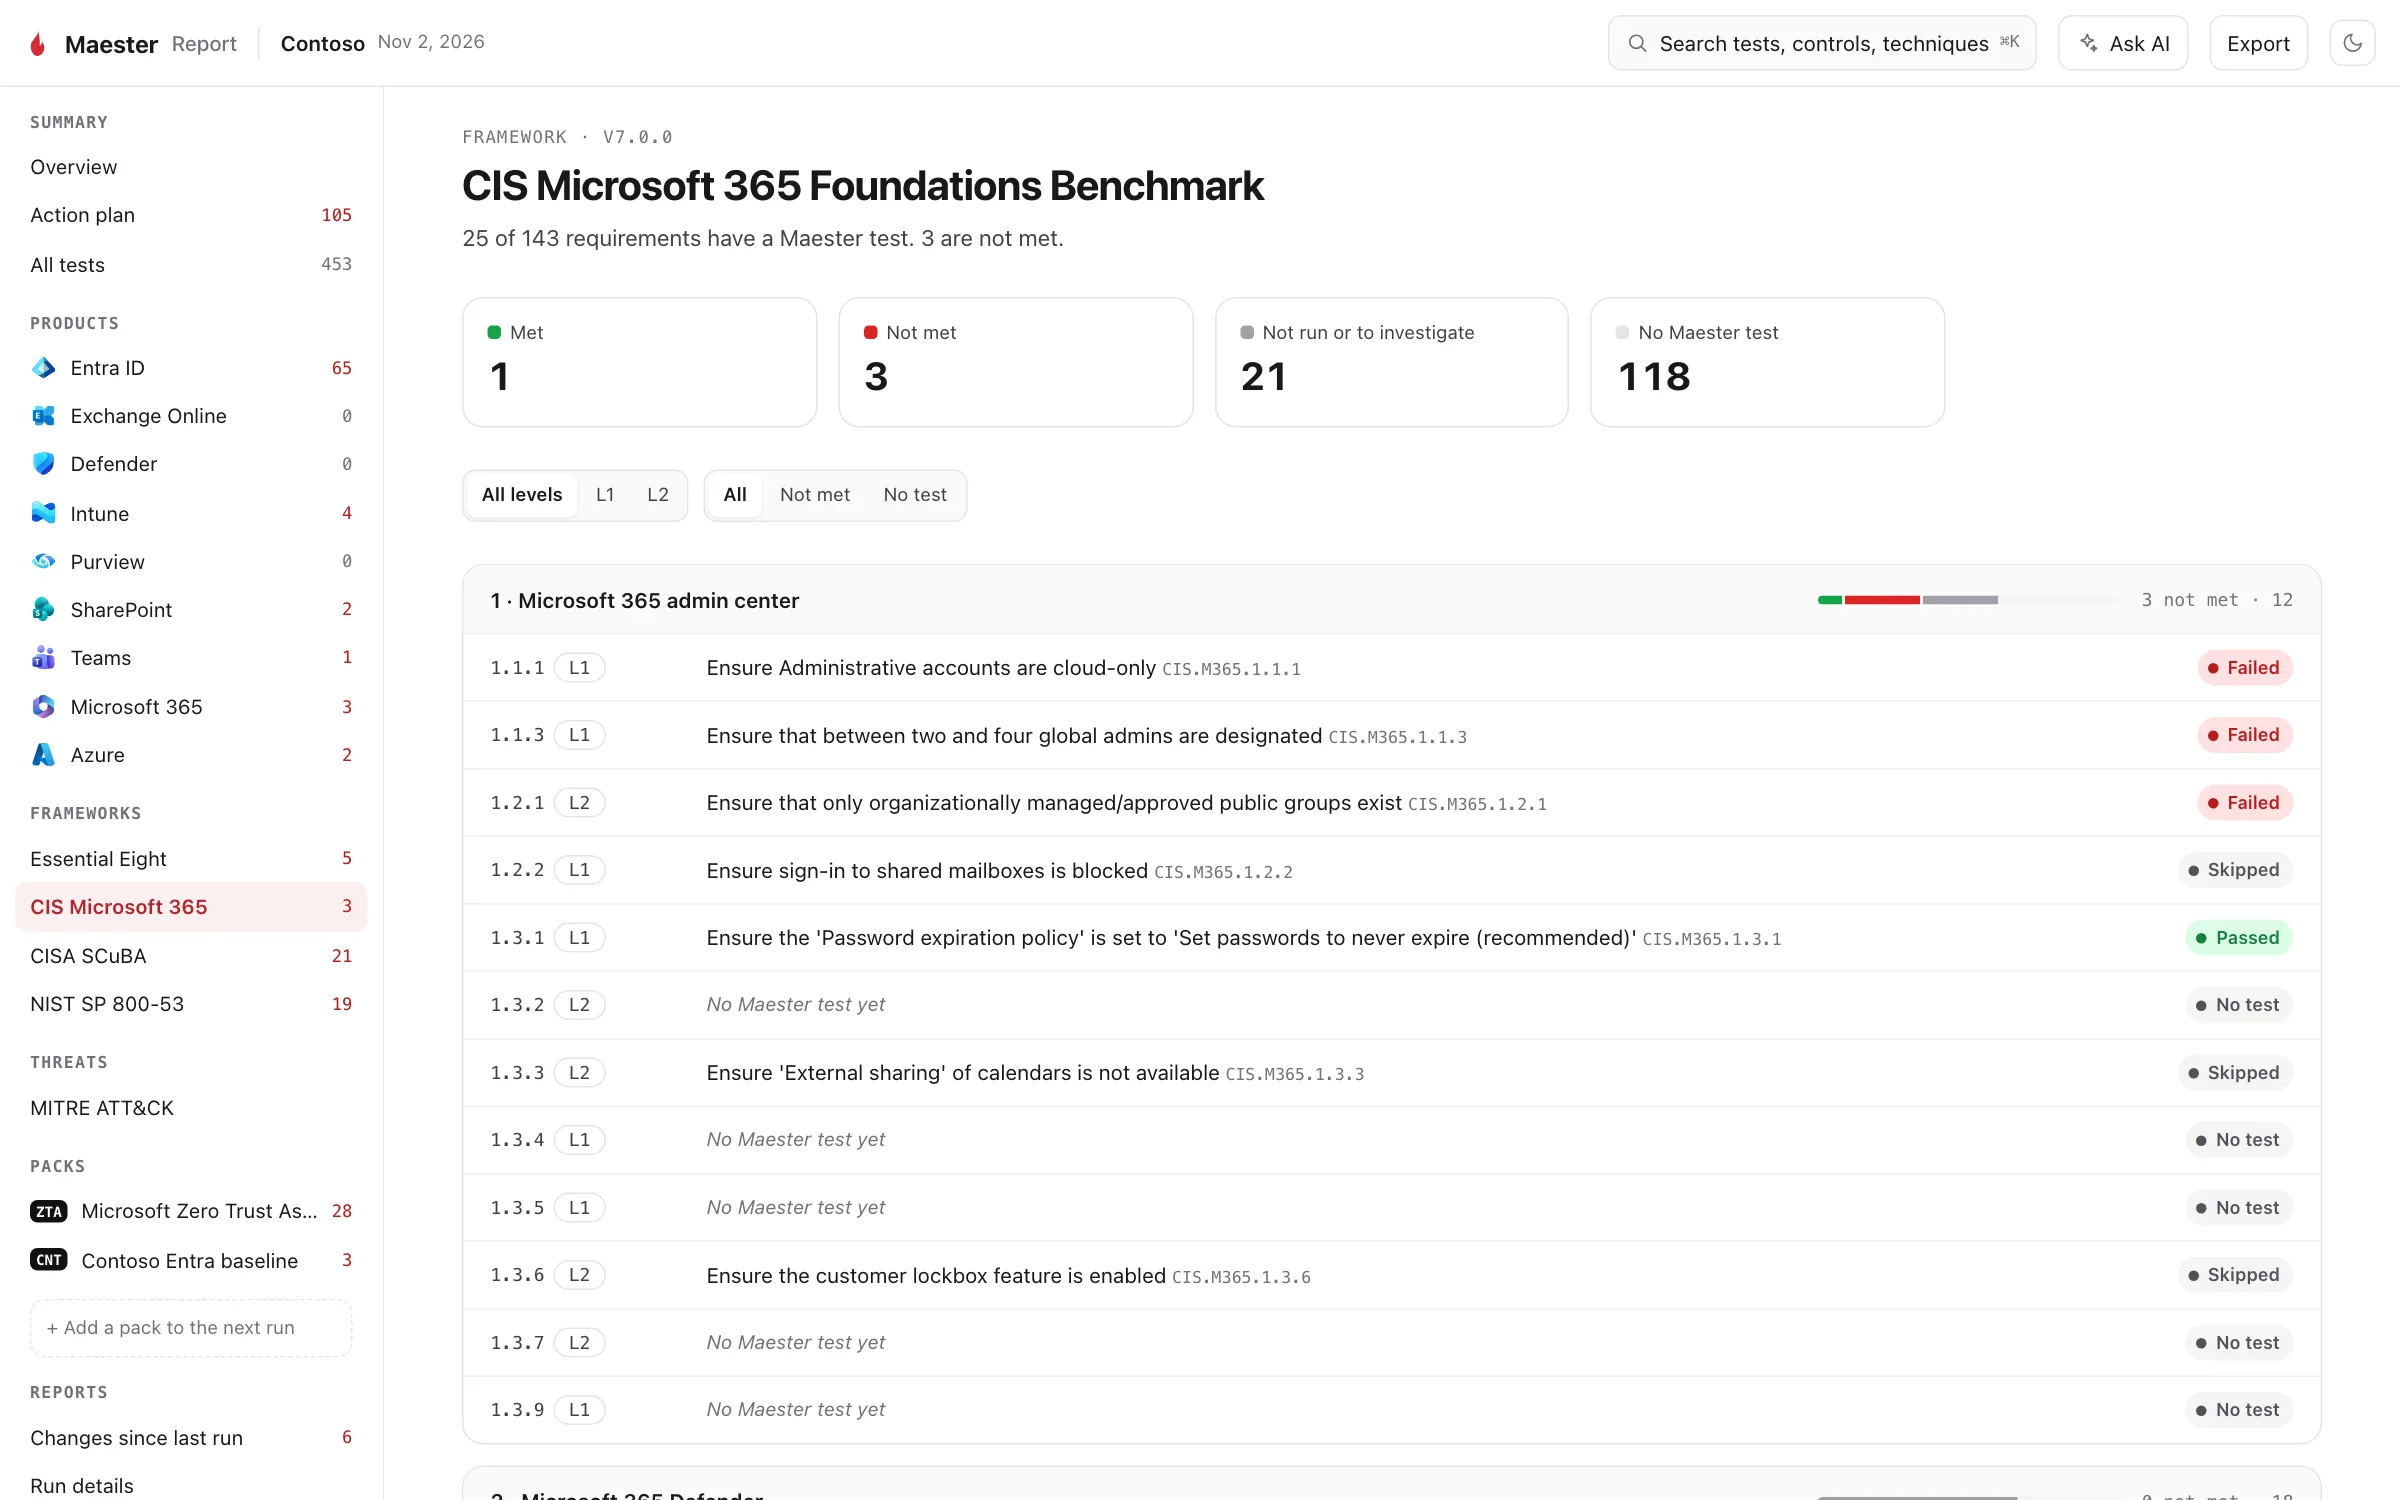
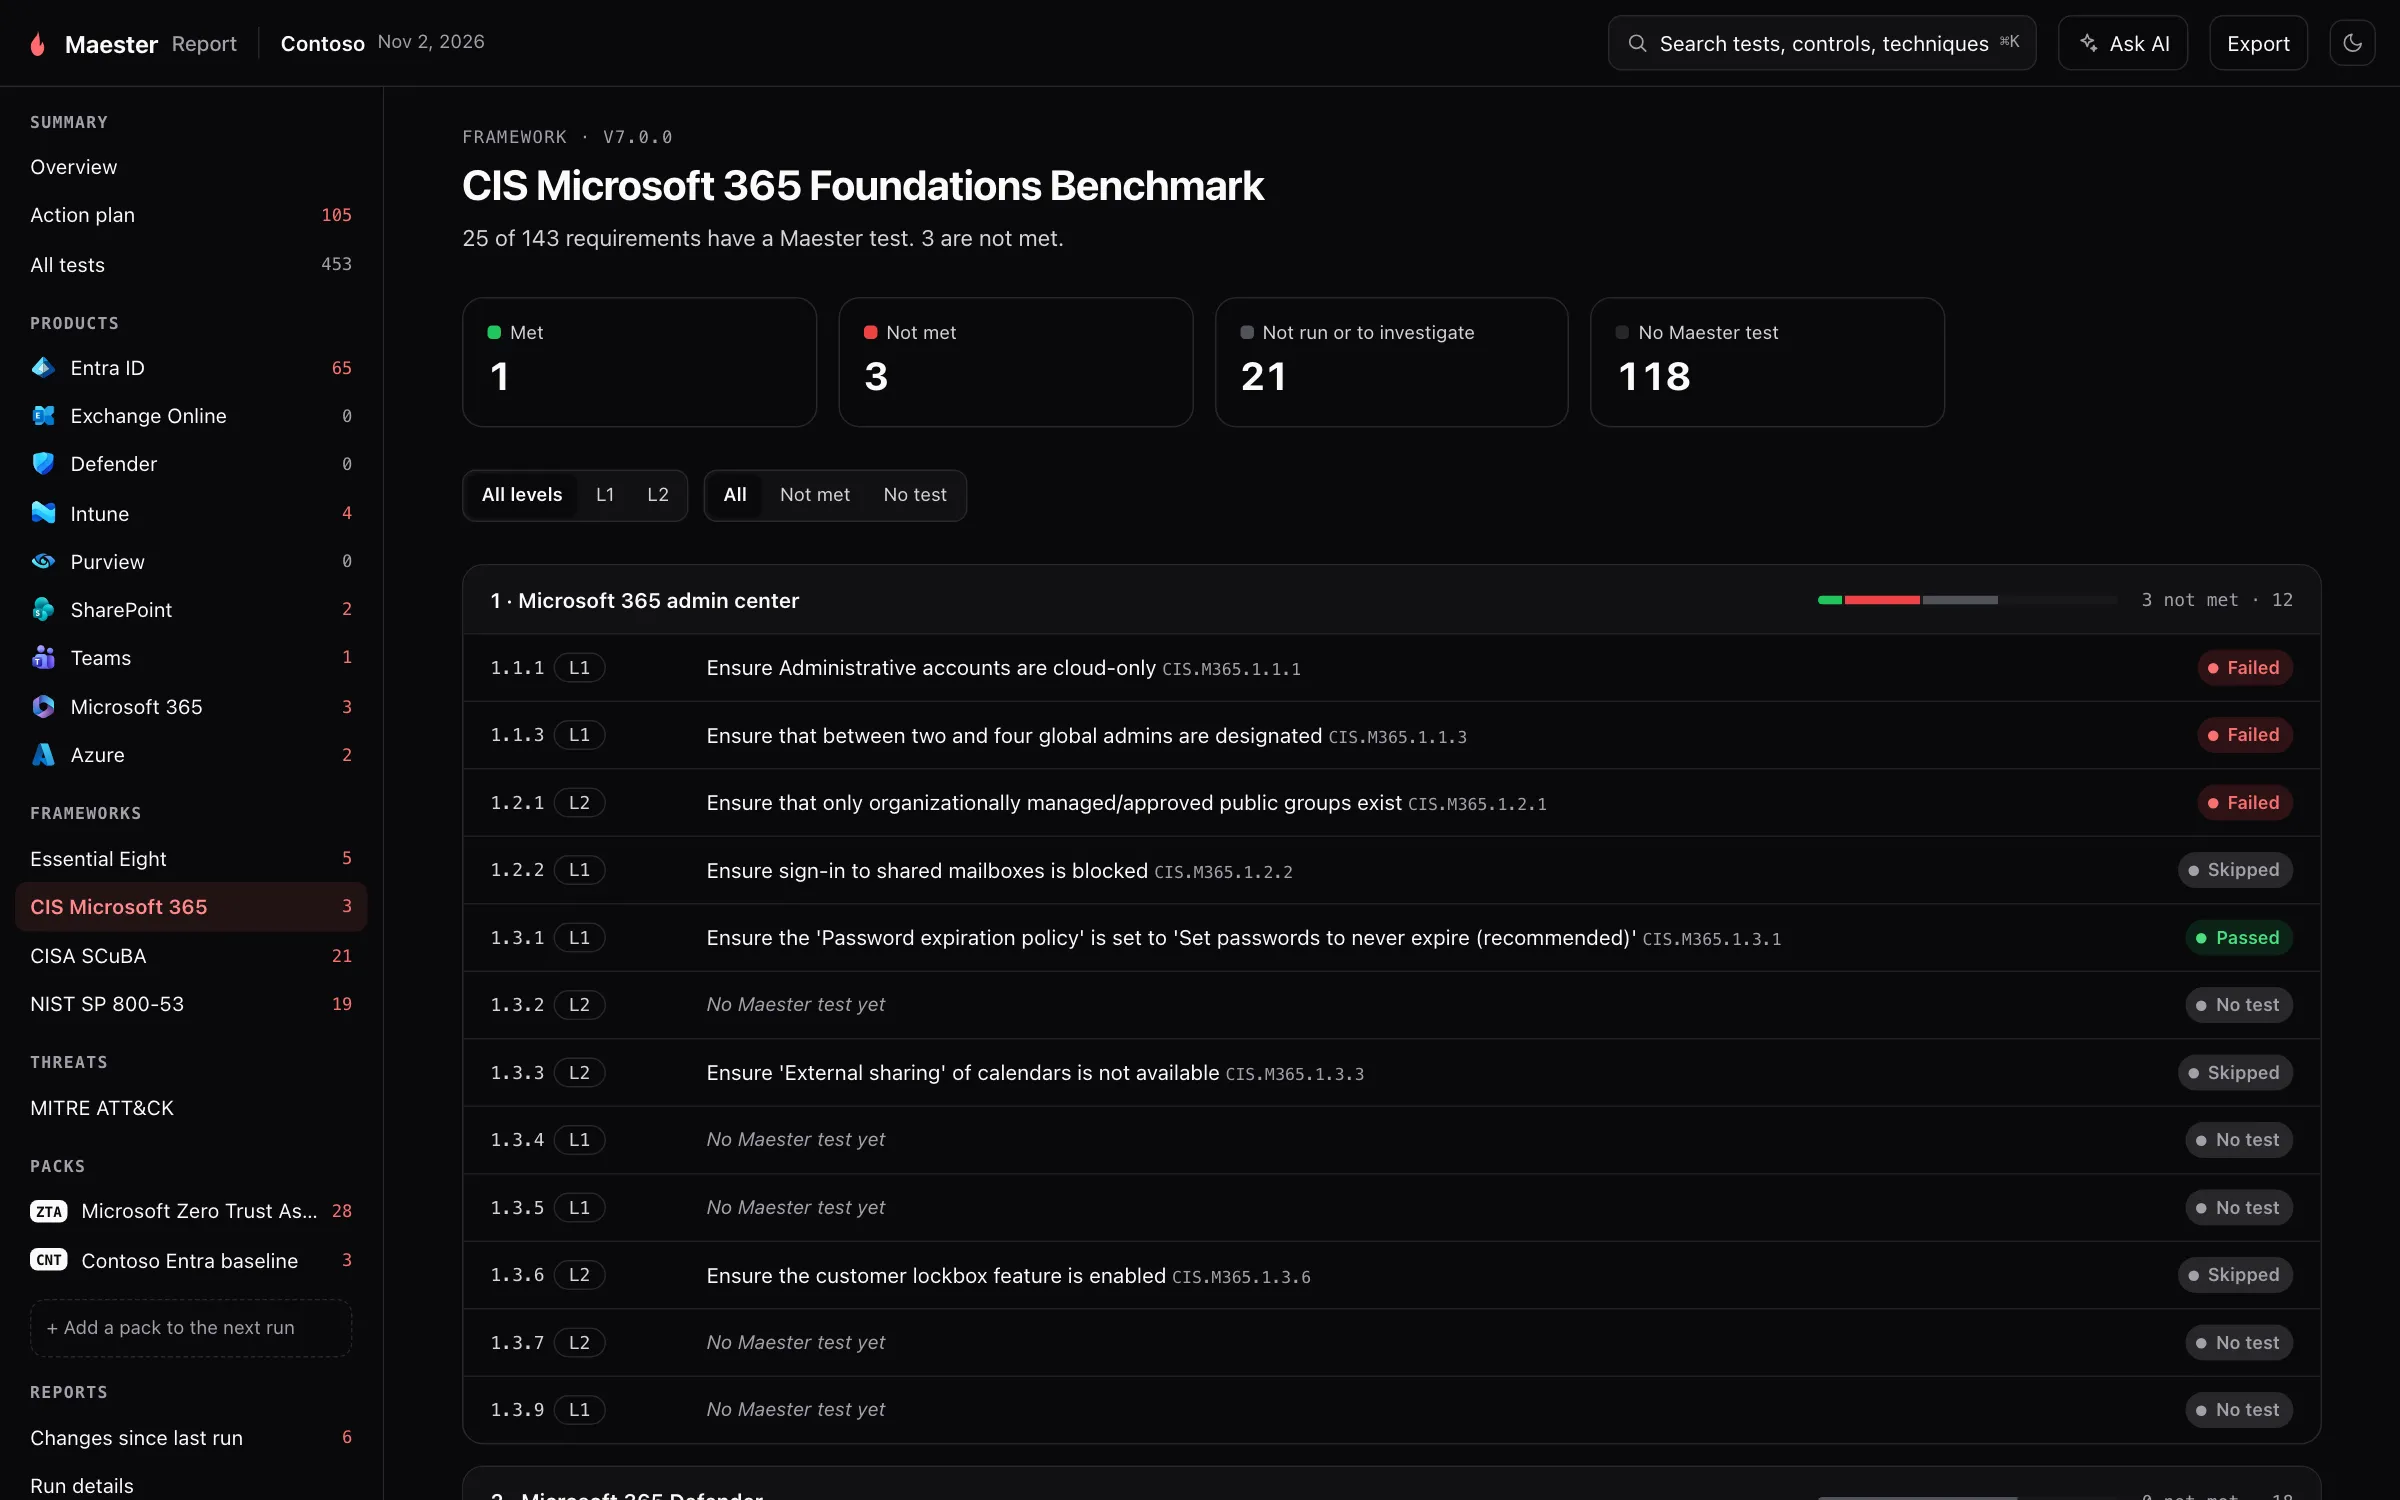
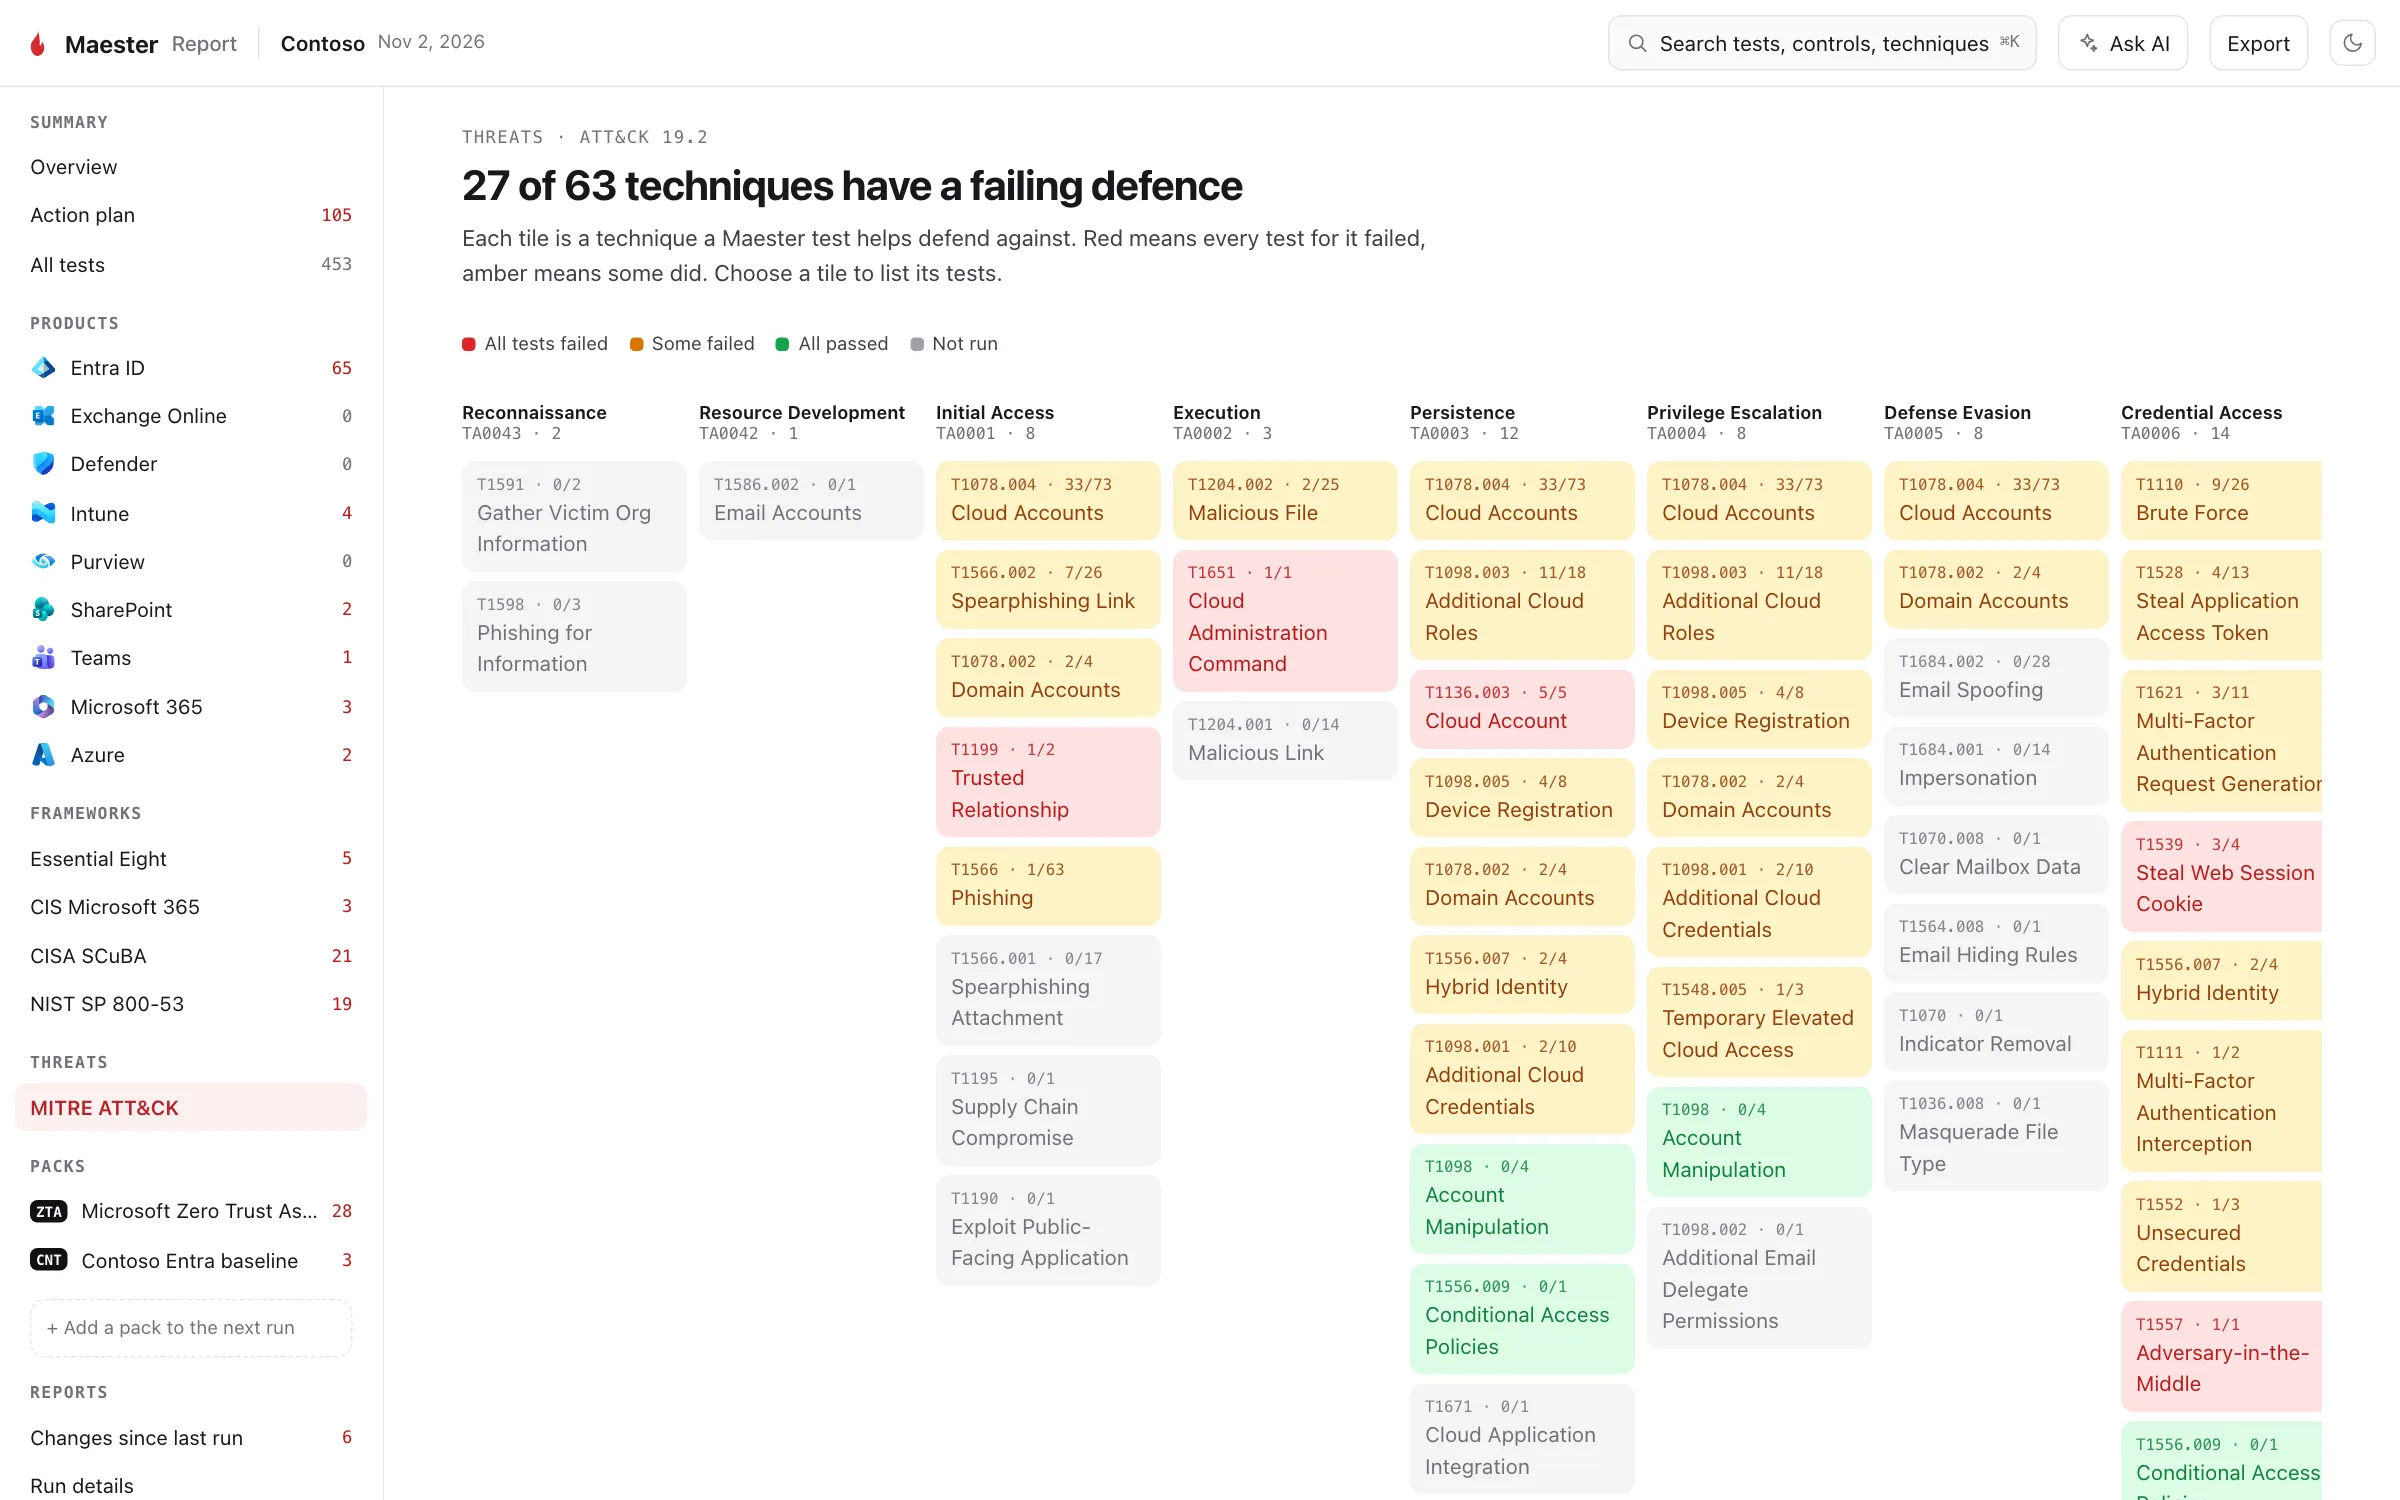
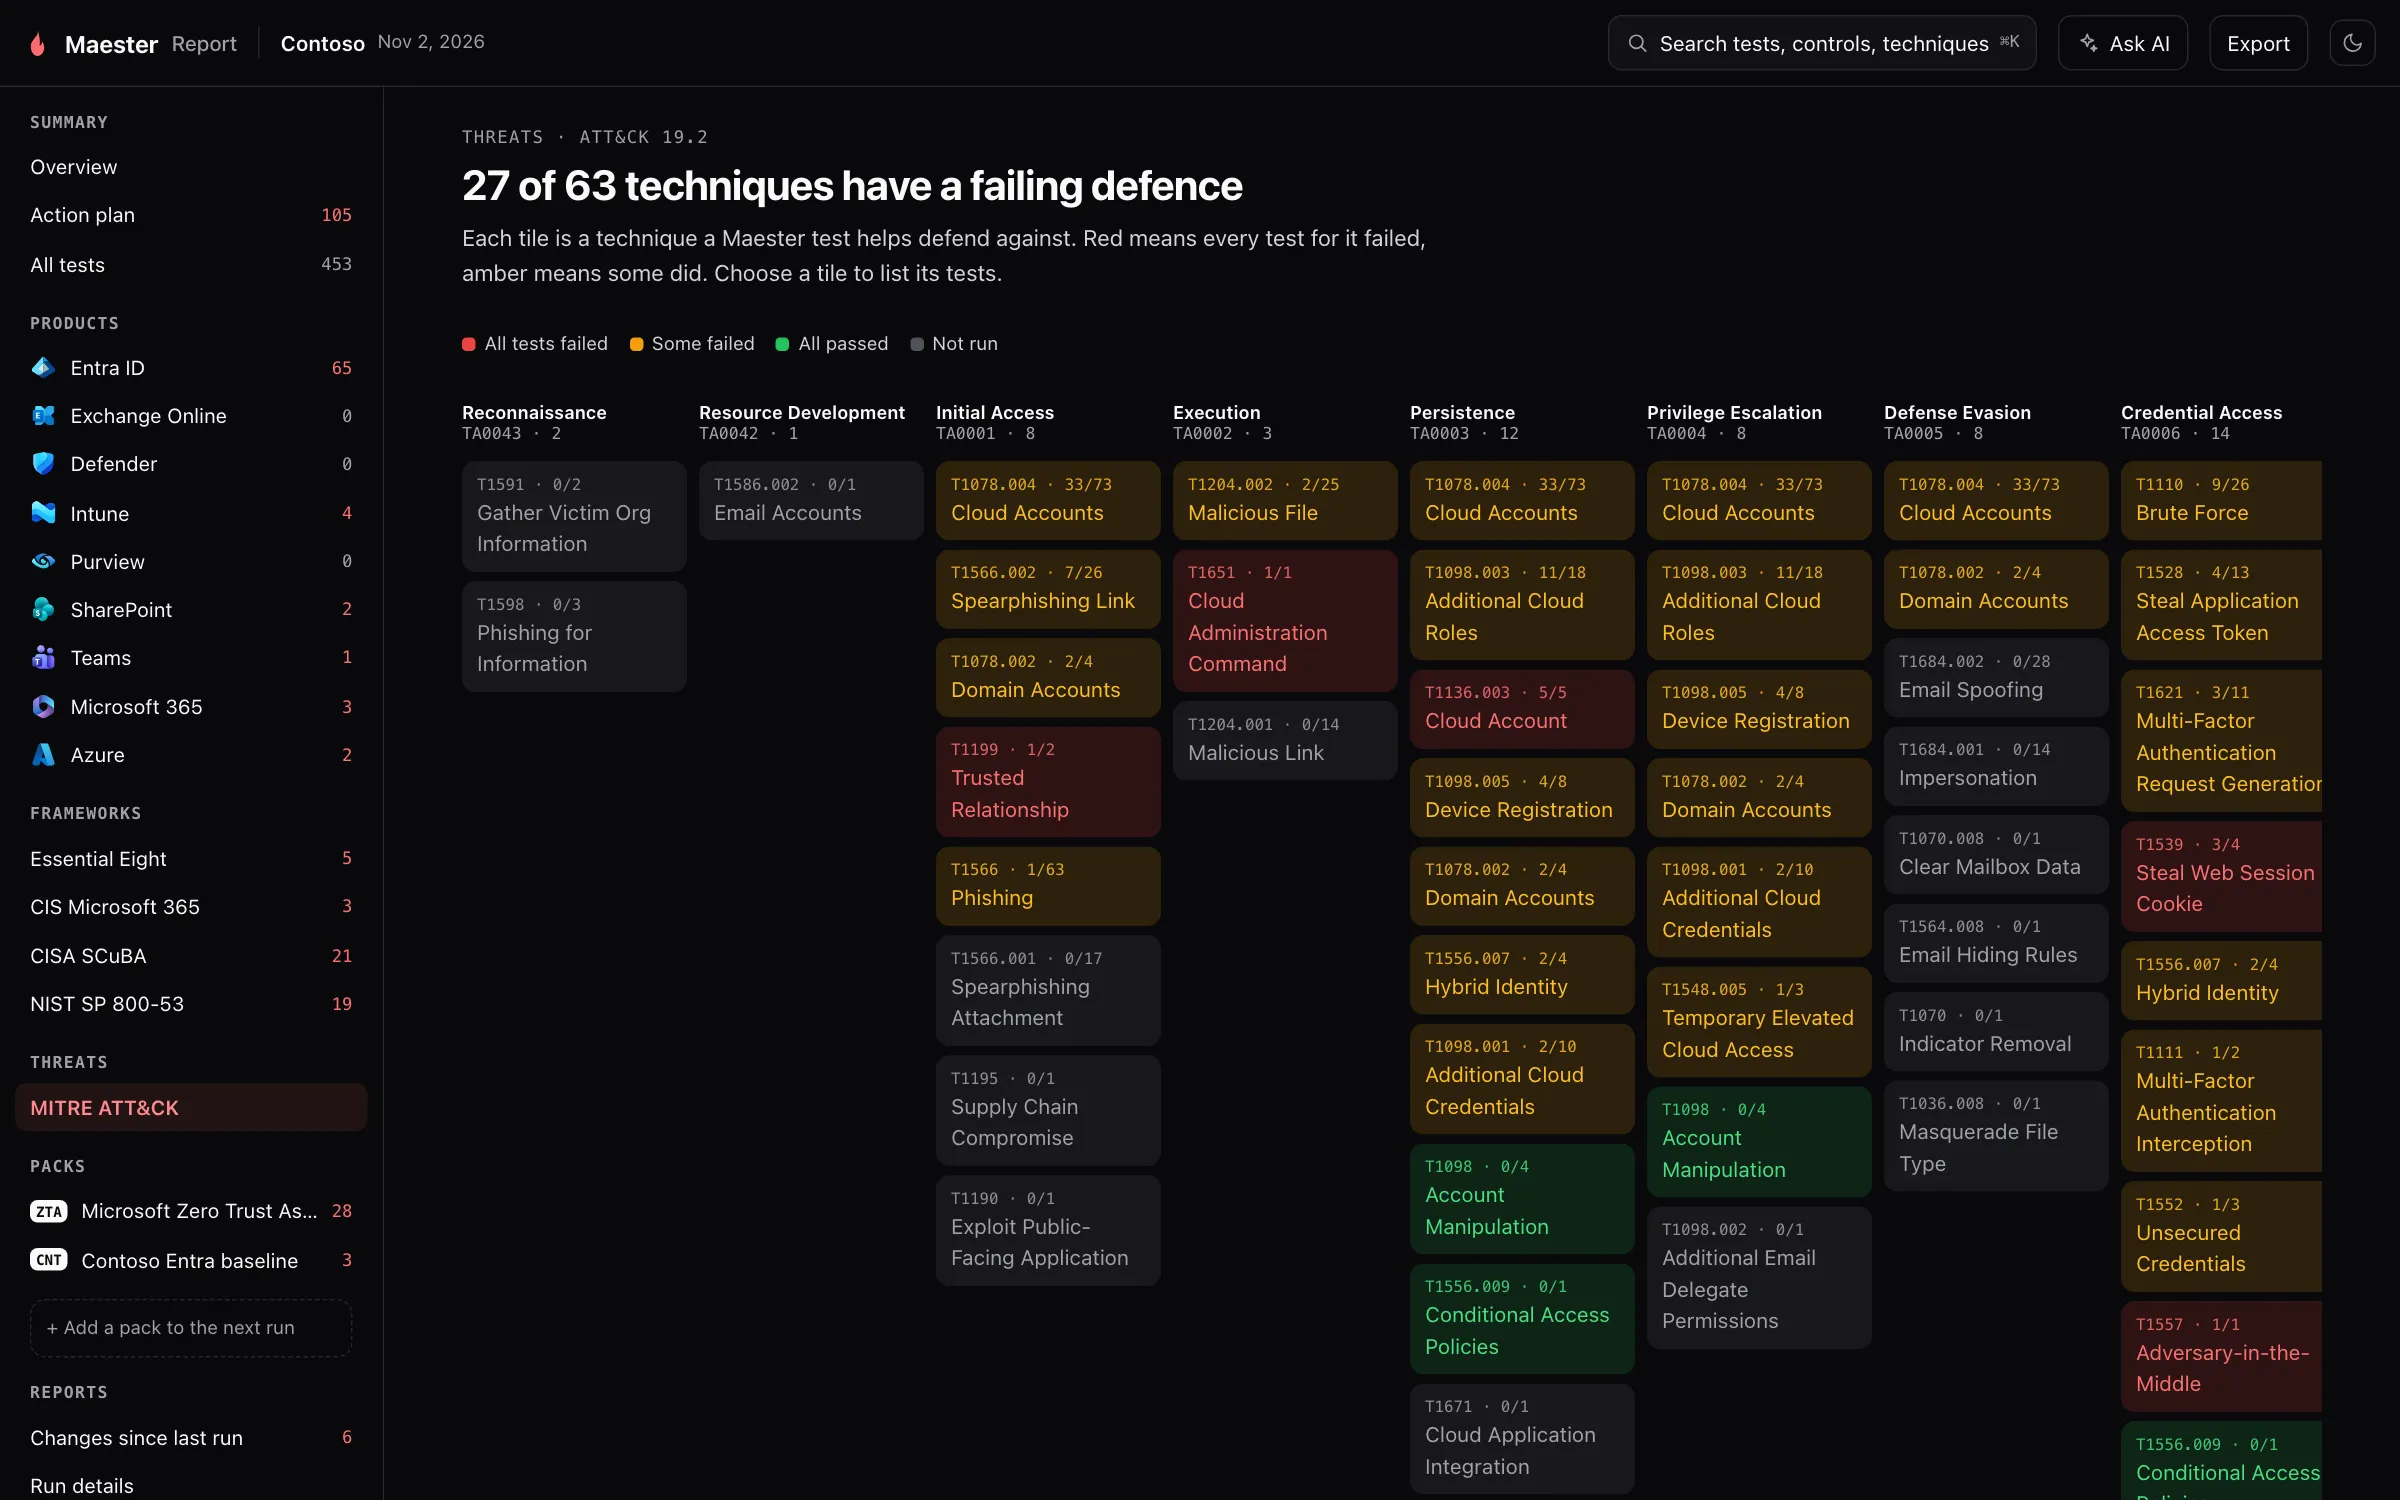
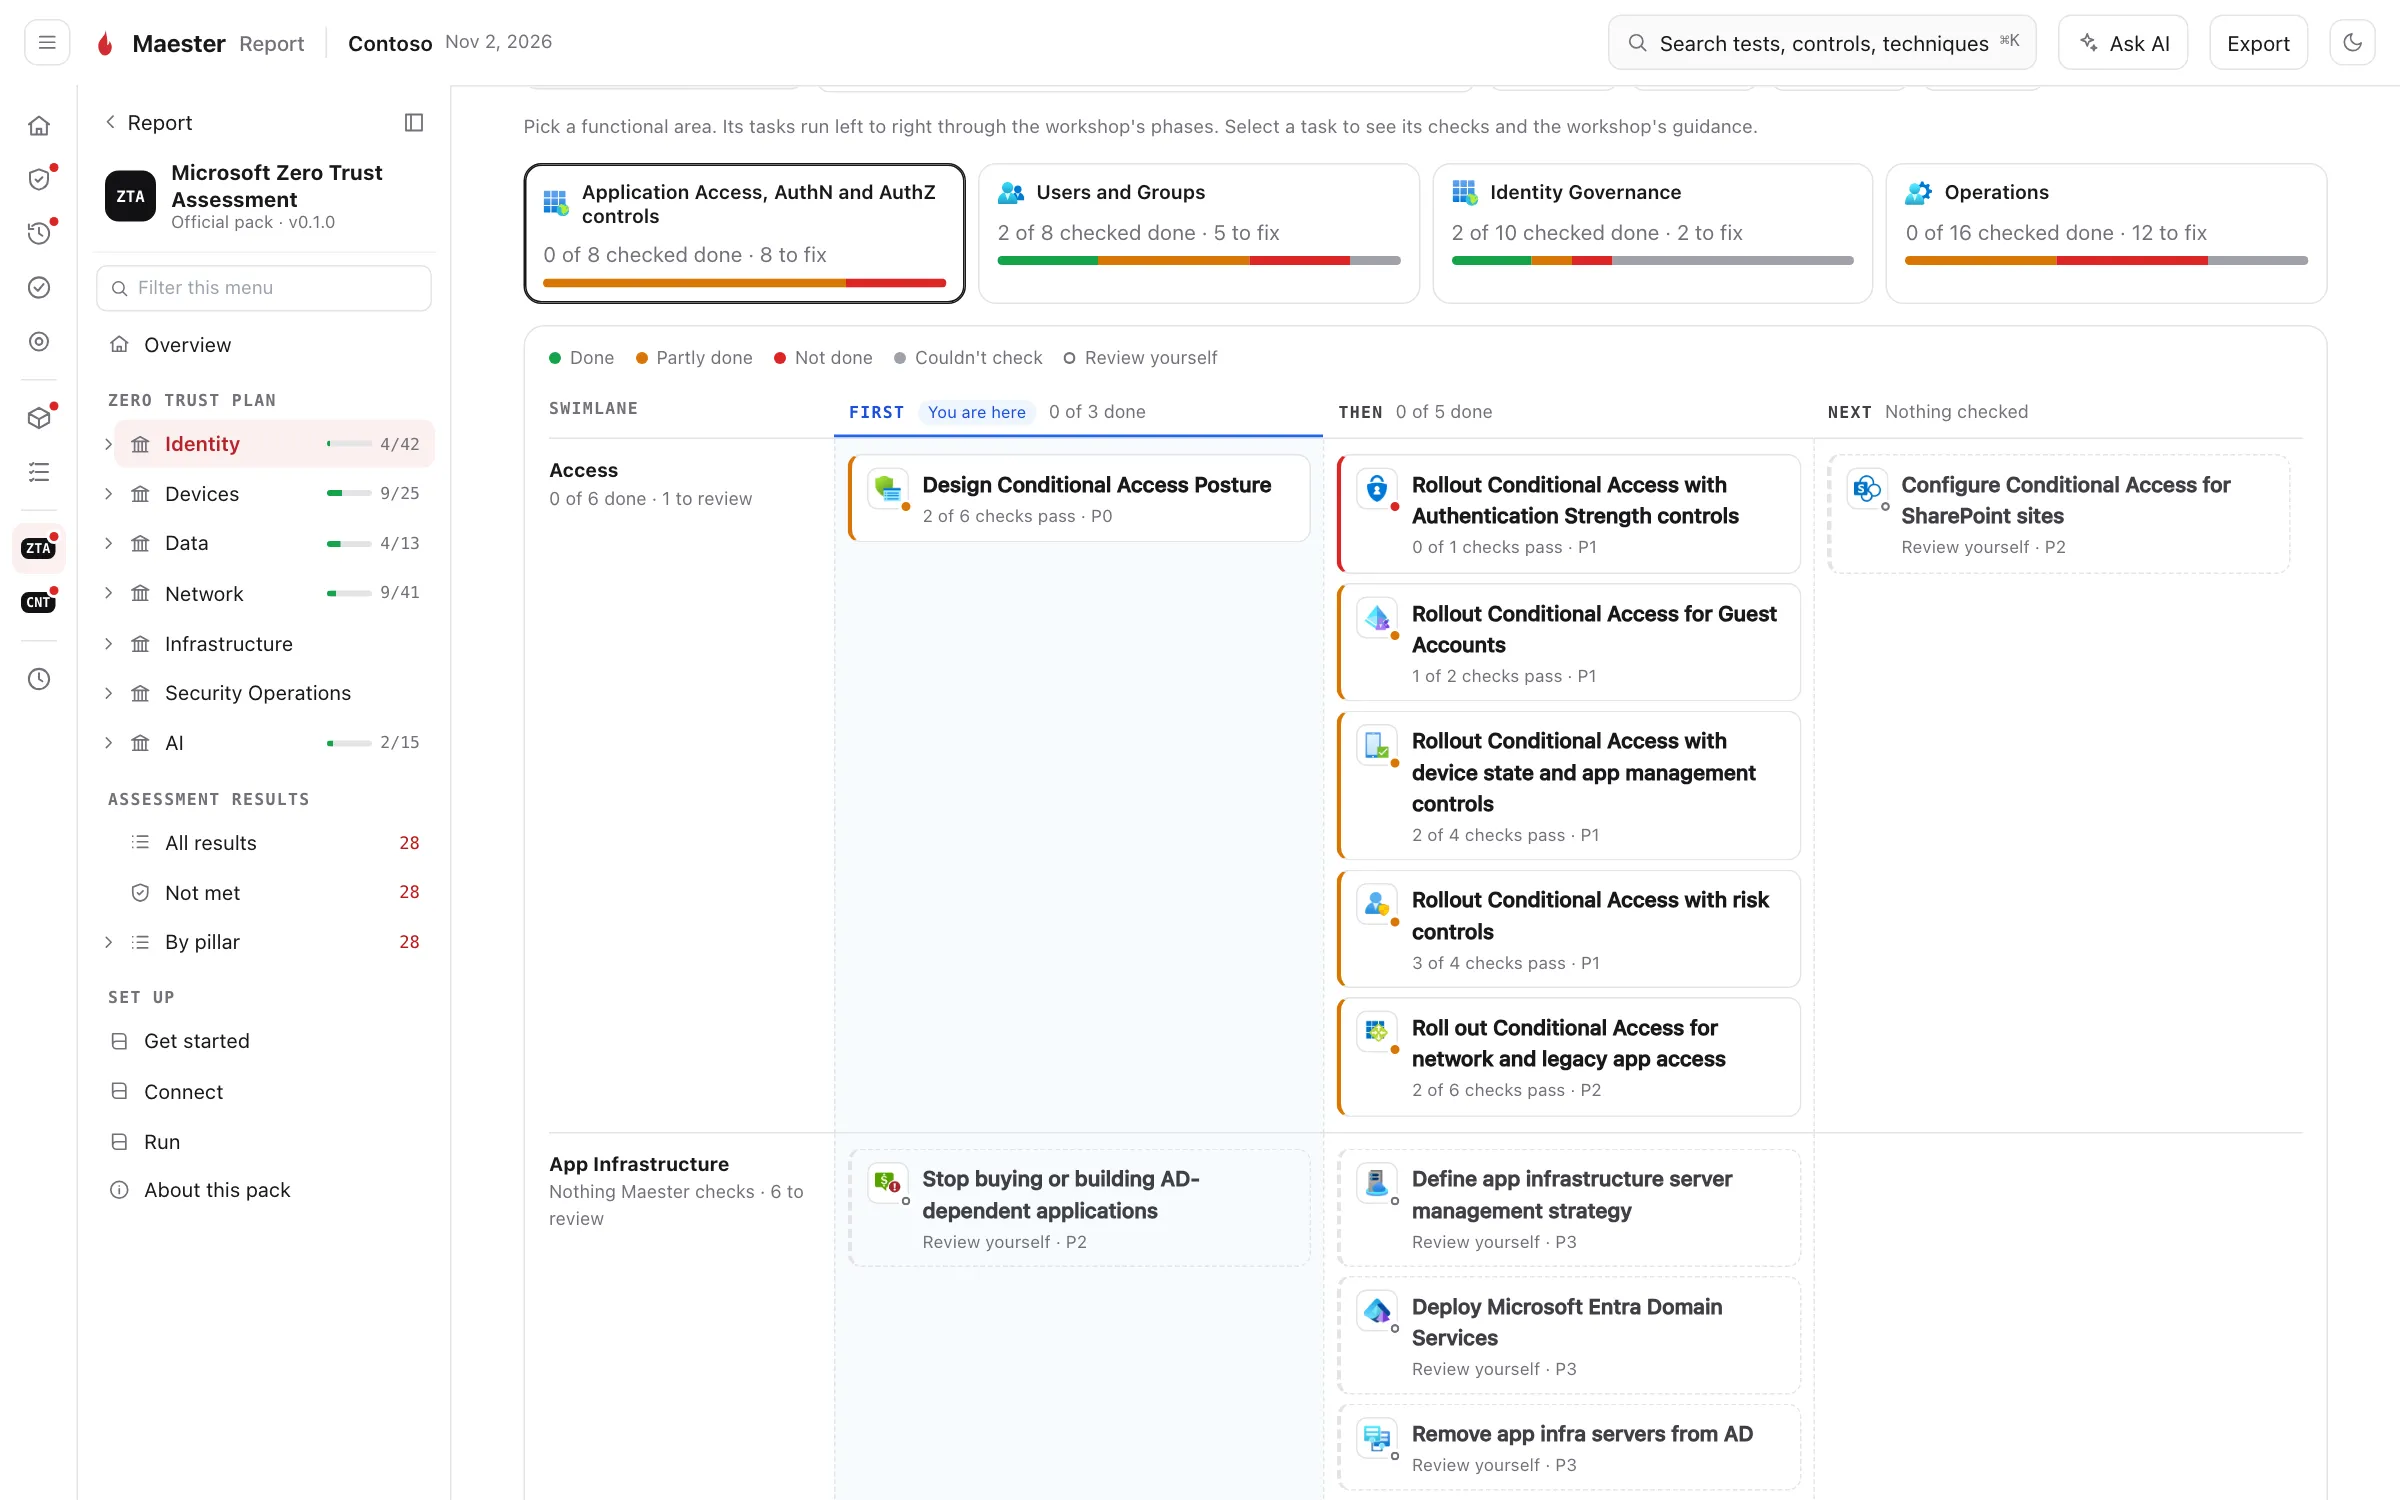
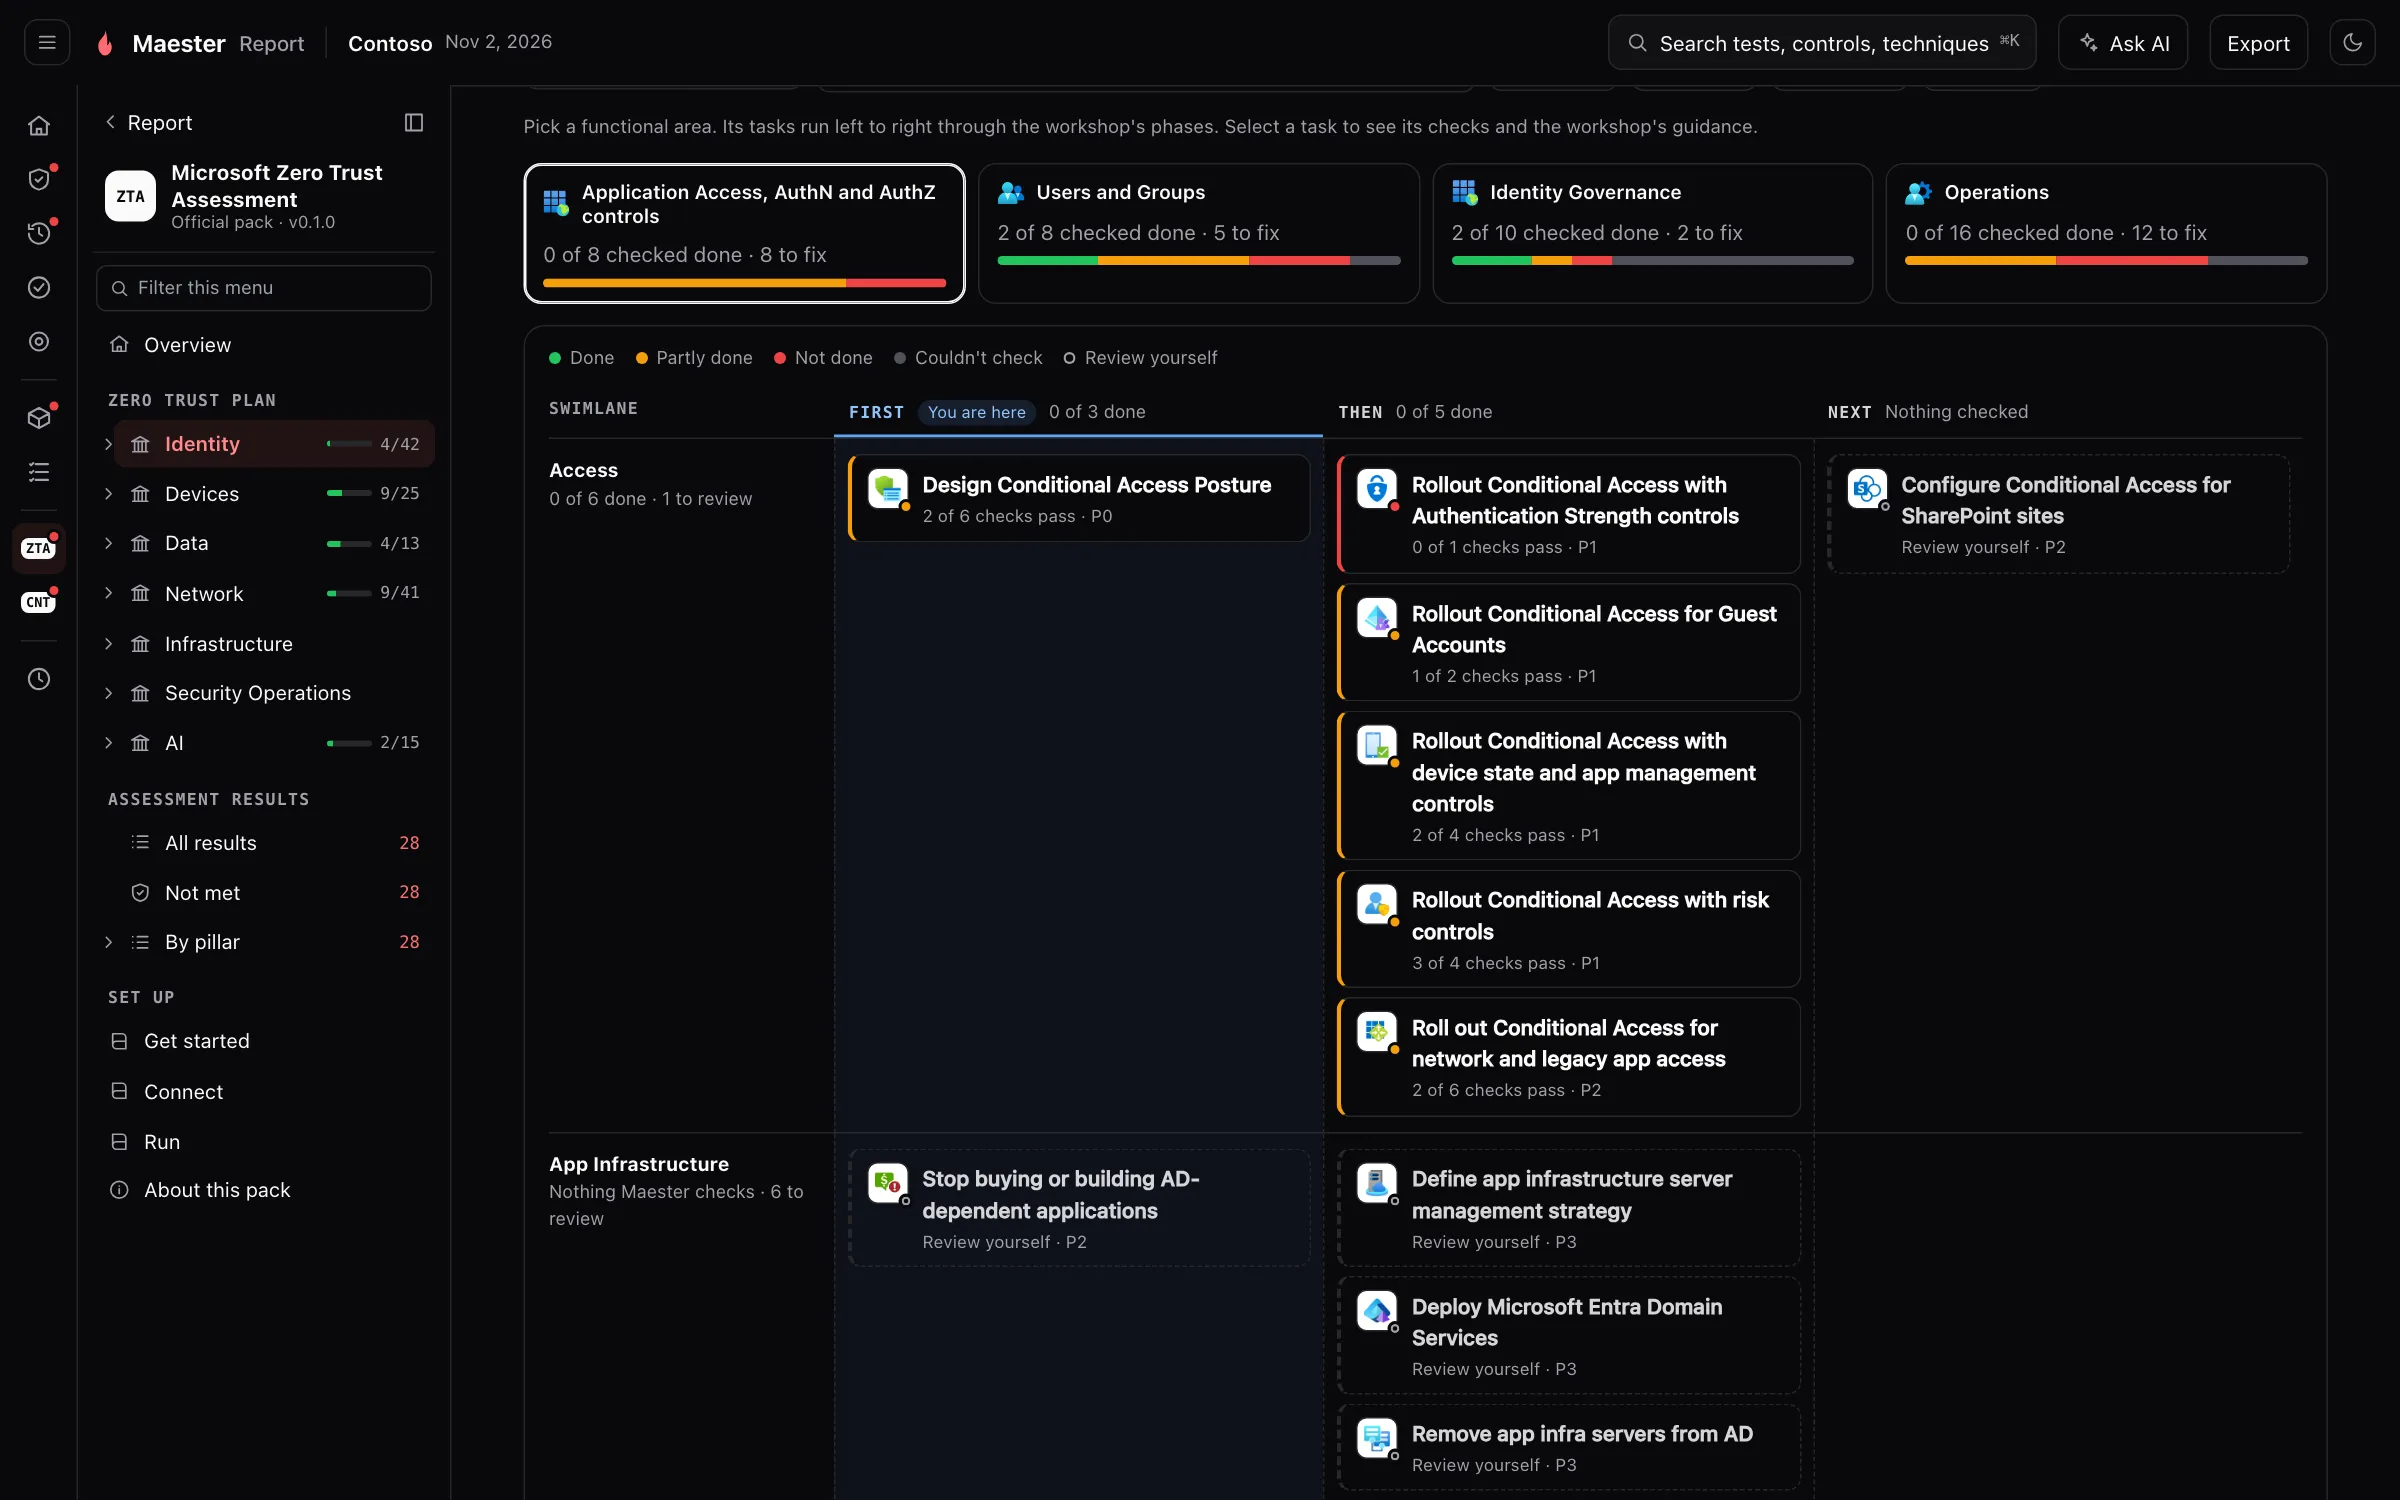
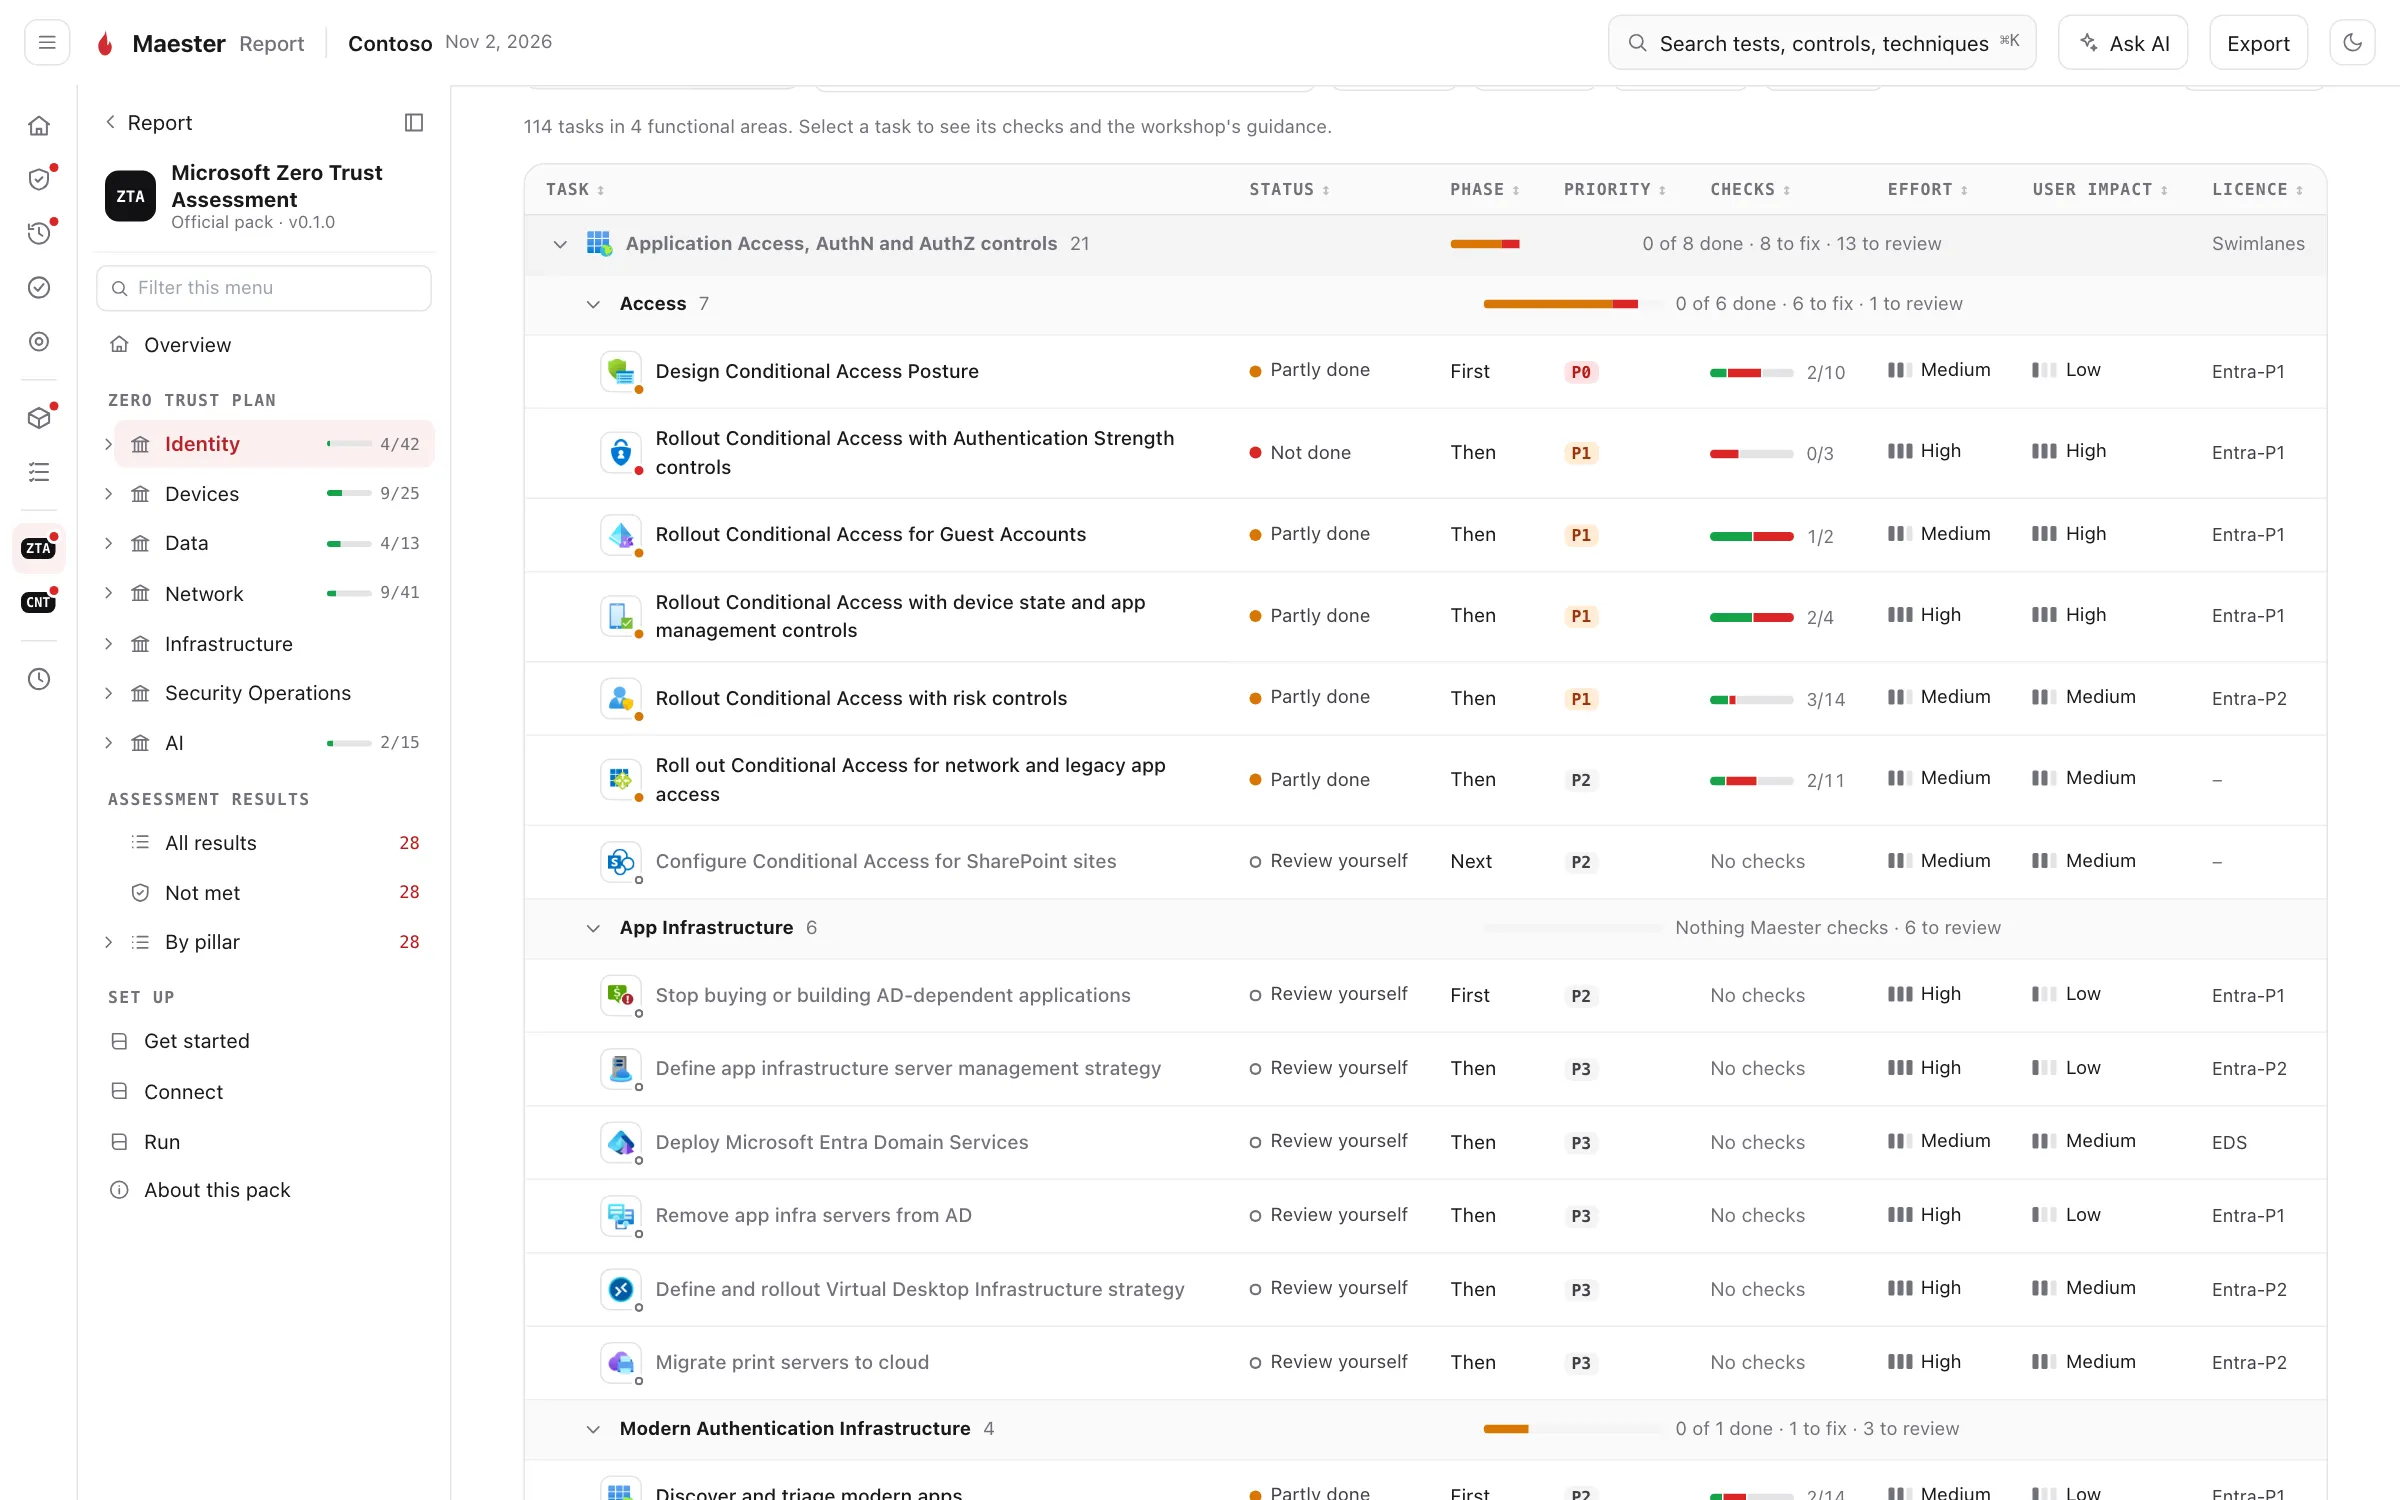
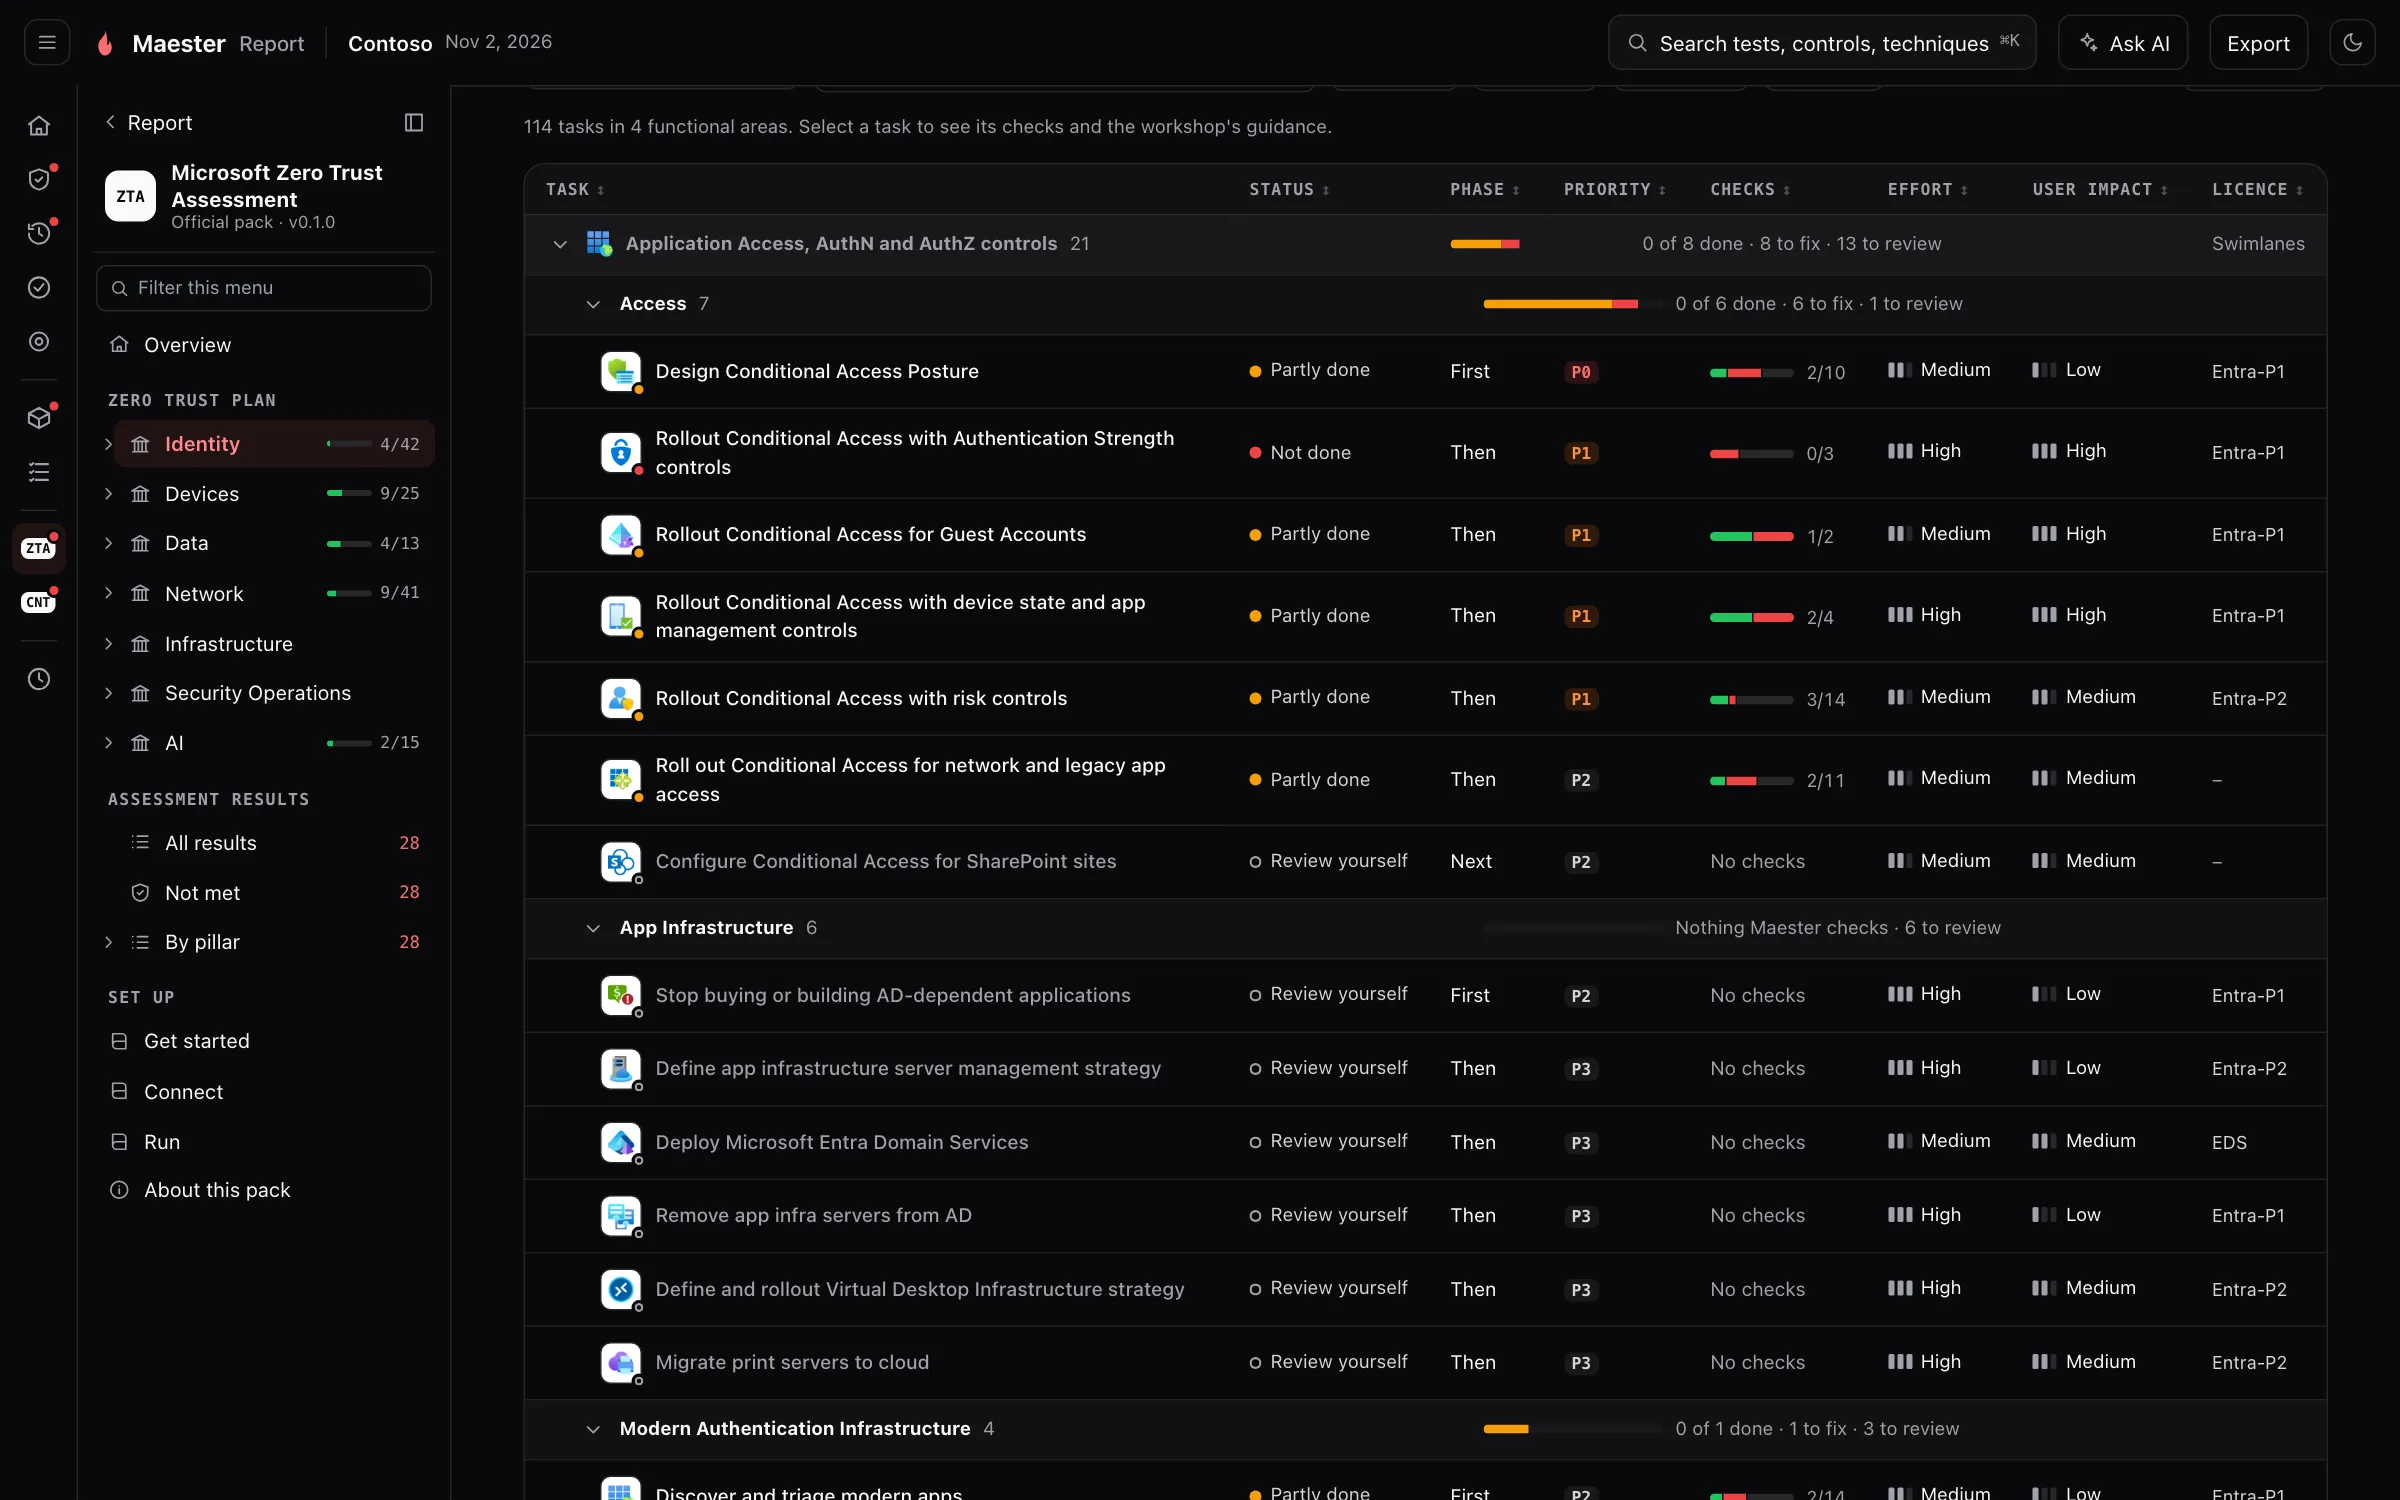
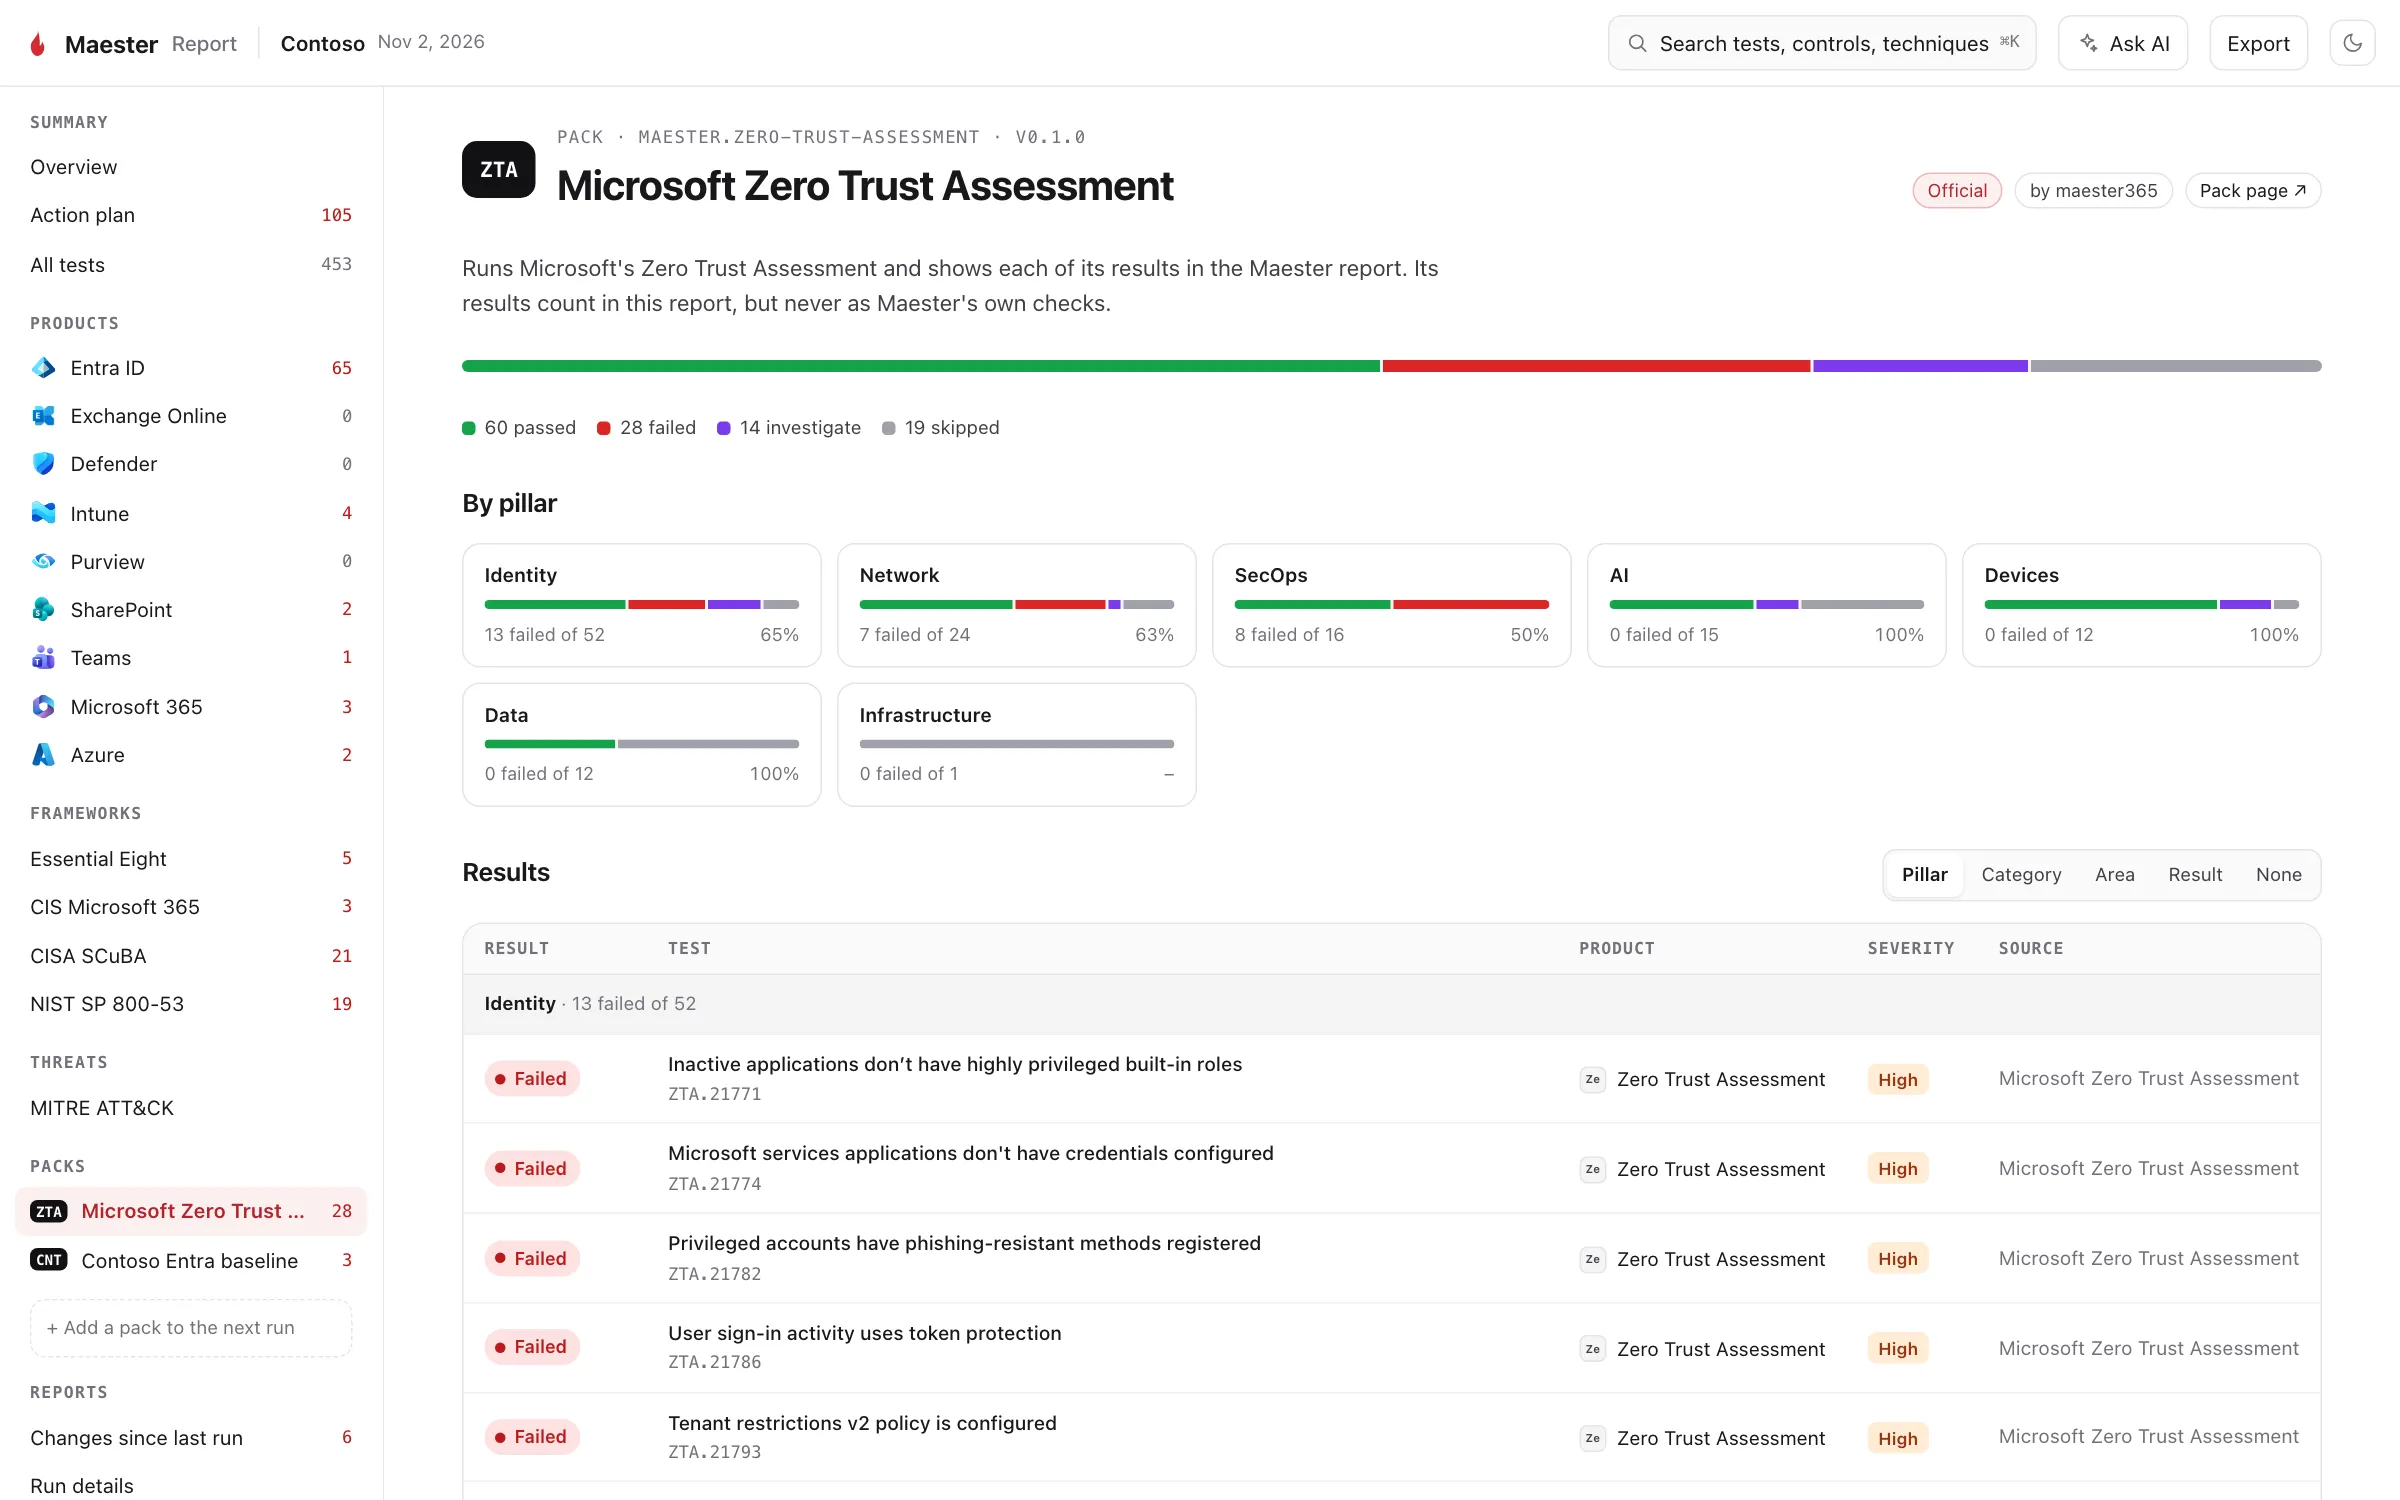
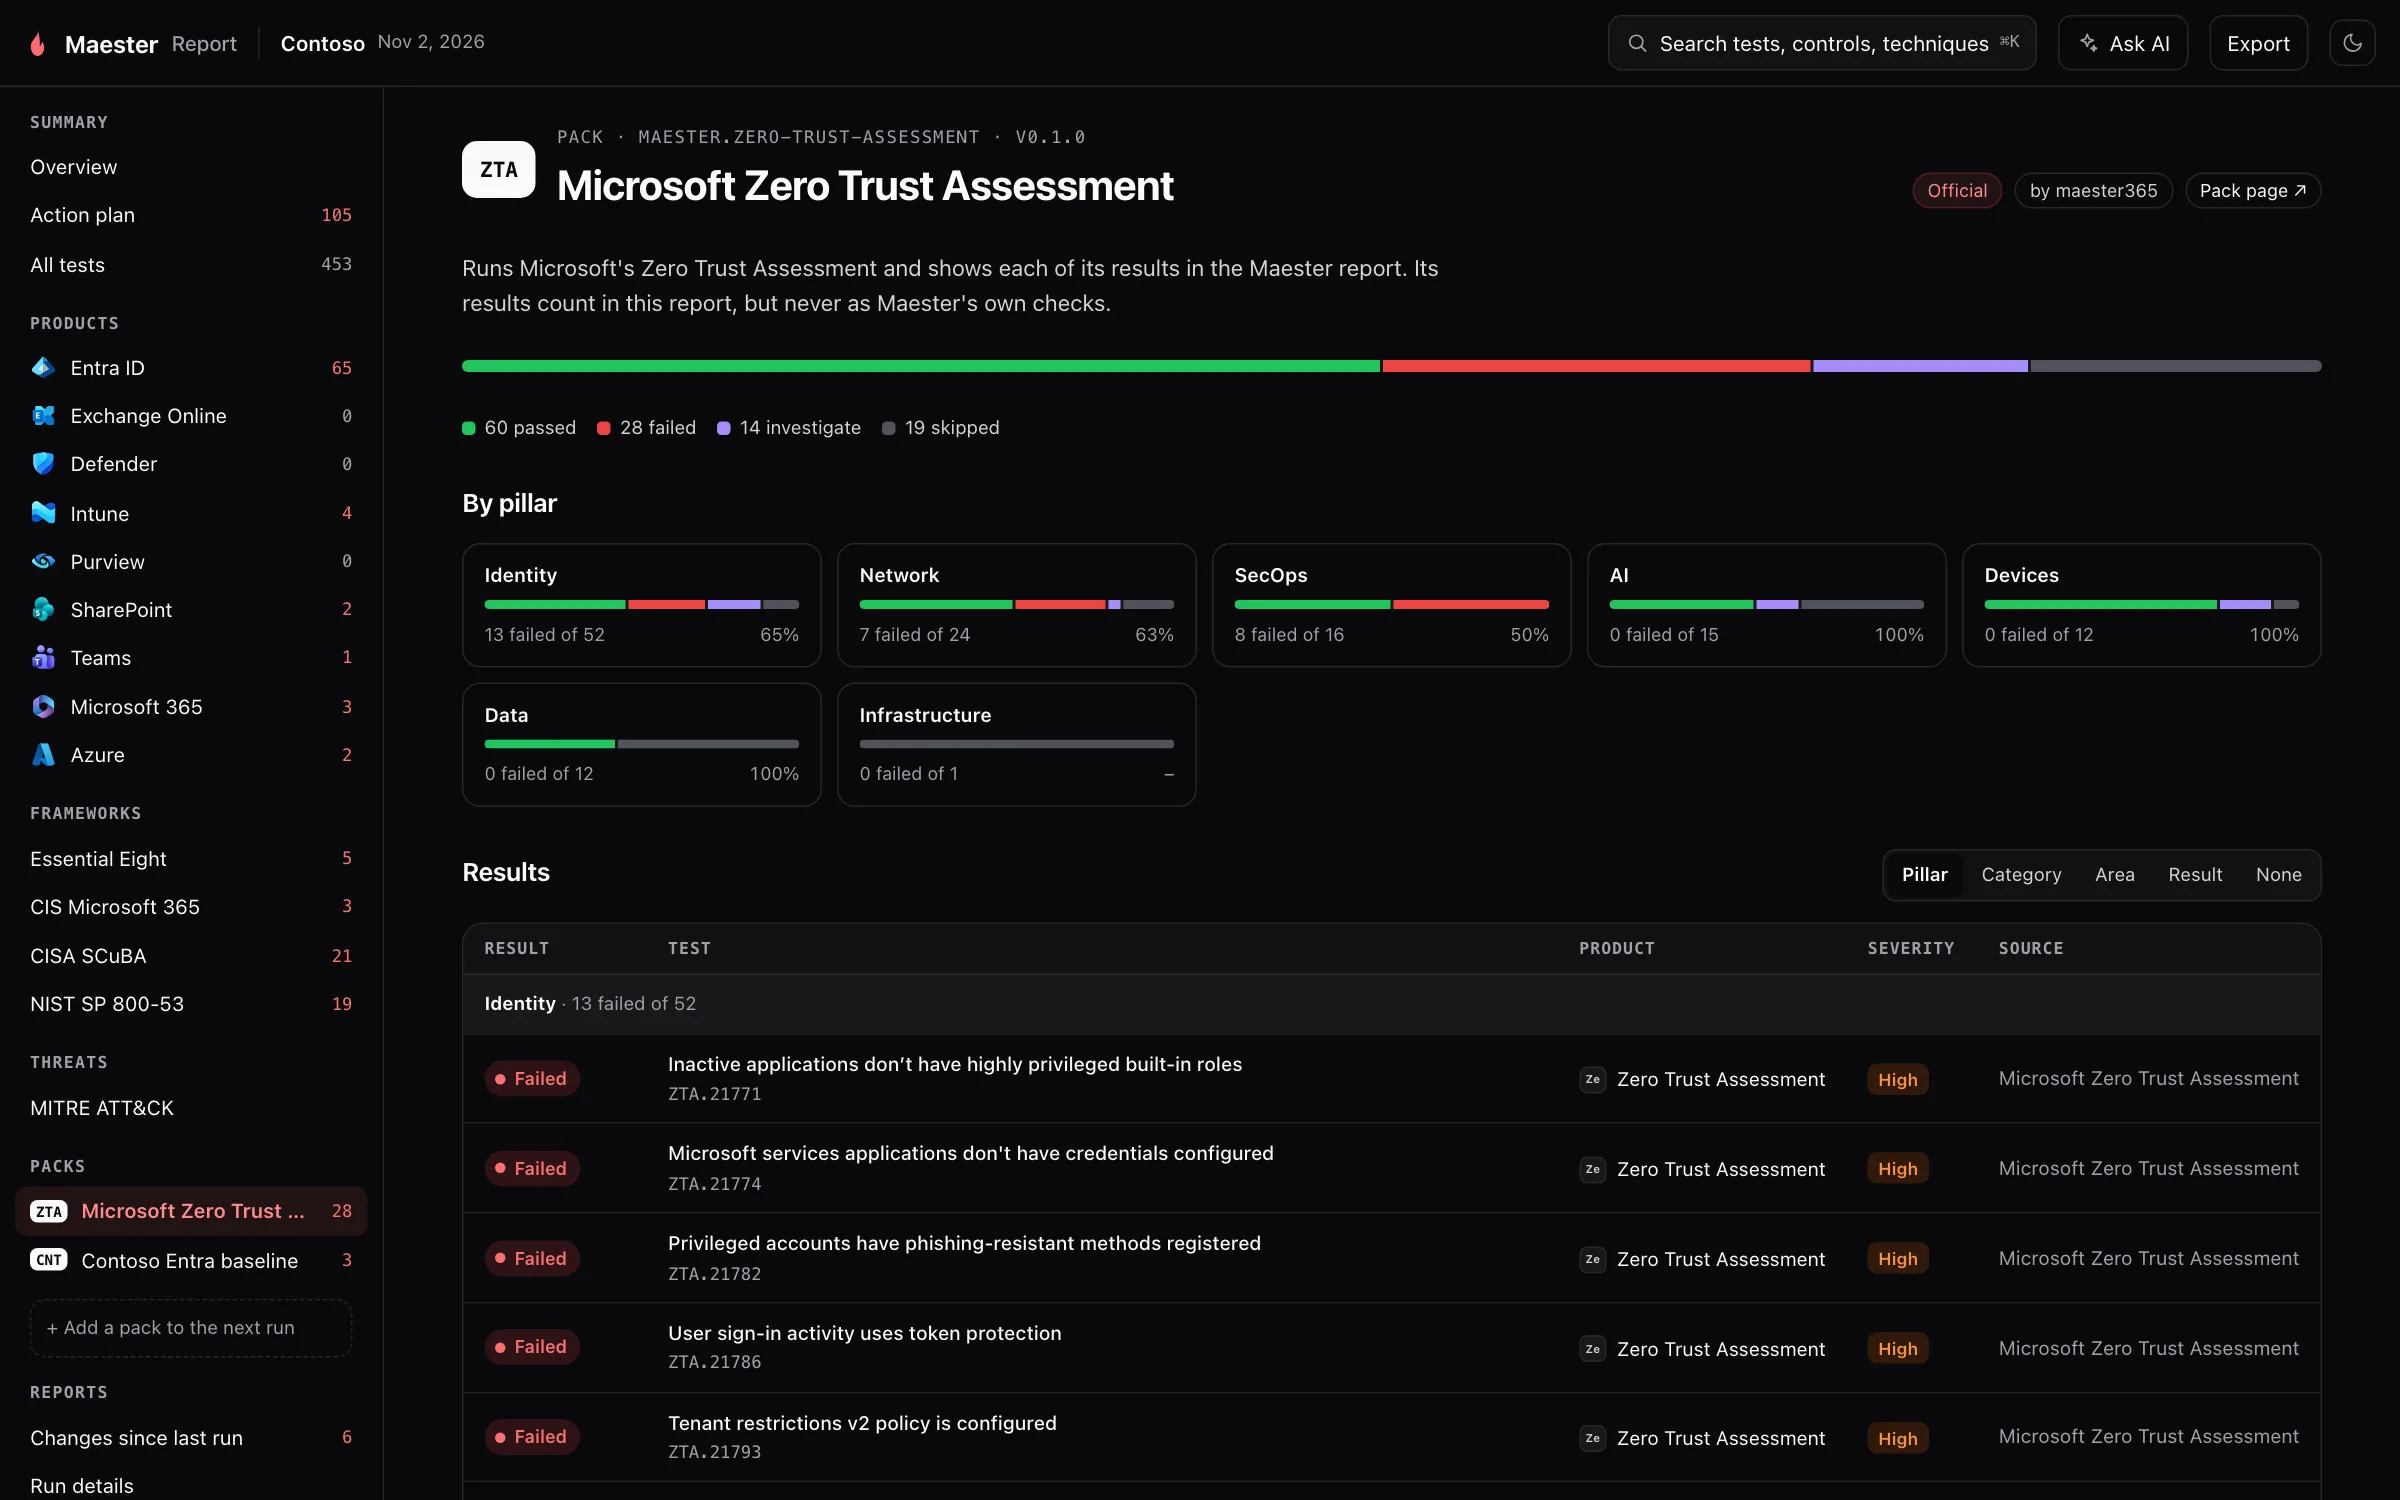
One page that says how your tenant is doing, what changed since the last run, and what to fix first.
01The checks
1,926 checks. Every framework your auditors ask about.
Each check names the requirement it implements, so one report answers CIS, CISA, Microsoft's Zero Trust Assessment, MITRE ATT&CK and NIST at once.
 Entra ID462
 Active Directory275
 Defender151
 Intune741
 Exchange Online61
 Azure59
 Purview46
 Azure DevOps46
 Teams23
 SharePoint20
02How it works
From install to a report in five minutes.
Then run it every night from the pipeline you already have.
Transcript
Maester. This is Maester: the open-source and most comprehensive way to test your Microsoft 365 security, every day, in one run.
Install. Install it from the PowerShell Gallery. Every check ships inside the module, so there's nothing else to set up.
Connect. Connect Maester to your tenant. It reads your configuration with read-only permissions, and nothing leaves your tenant.
Run. Now run Invoke-Maester. Add the Zero Trust Assessment pack, and Microsoft's own assessment runs in the same pass.
Watch it run. The console shows every product as it's tested, the checks running right now, and the results as they land: over twelve hundred checks across CIS, CISA, Microsoft's guidance and Zero Trust.
The report. When the run finishes, your report opens. It tells you what to fix first, ranked by severity and effort.
Every finding. Every finding explains what an attacker could do, what Maester found, and exactly how to fix it.
Frameworks. See where you stand against the frameworks your auditors ask about, and the attack techniques each gap leaves open.
Zero Trust. And Microsoft's Zero Trust Assessment sits right alongside, in the same report.
Automate. Run it every day in GitHub Actions or Azure DevOps, and know the moment something changes.
Maester Cloud. Or run it with Maester Cloud, securely, in your own Azure subscription: your data never leaves your tenant. Find out more at maester.cloud, and get started at maester.dev.
- 1Install
Install-Module Maester - 2Connect
Connect-Maester - 3Run
Invoke-Maester -Pack ZTA - 4Automate
maester-action@main
Runs in GitHub Actions, Azure DevOps, Azure Automation, Azure Container Apps, GitLab, Bitbucket and Terraform, and sends results to email, Teams and Slack.
03Maester Packs
Need a check Maester doesn't have? Add a pack.
Packs add checks from Microsoft and the community, in the same report. The community's CIS Intune benchmark packs add 631 device checks on their own, one for each setting.
 Community pack · 307 checksCIS Windows 11 Intune L1Checks that Intune policies configure the Level 1 recommendations of the CIS Microsoft Intune for Windows 11 Benchmark v5.0.0. One test per setting.by Pacers31Colts18
 Community pack · 26 checksUser AttributesChecks that Microsoft Entra users have the attributes HR processes, dynamic groups and licensing depend on, that those values are formatted consistently, and that they use your approved values and office locations.by DevClate
 Community pack · 5 checksLeast Privileged MSGraphChecks that service principals hold only the Microsoft Graph permissions their real API activity needs, using Microsoft Graph activity logs in Log Analytics.by Mynster9361
 Community pack · 8 checksRKSolutions Intune AnomaliesFinds what needs attention in Microsoft Intune before it becomes a problem: devices that miss protection, drift out of compliance or fall out of management, and policies that still rely on outdated settings.by royklo
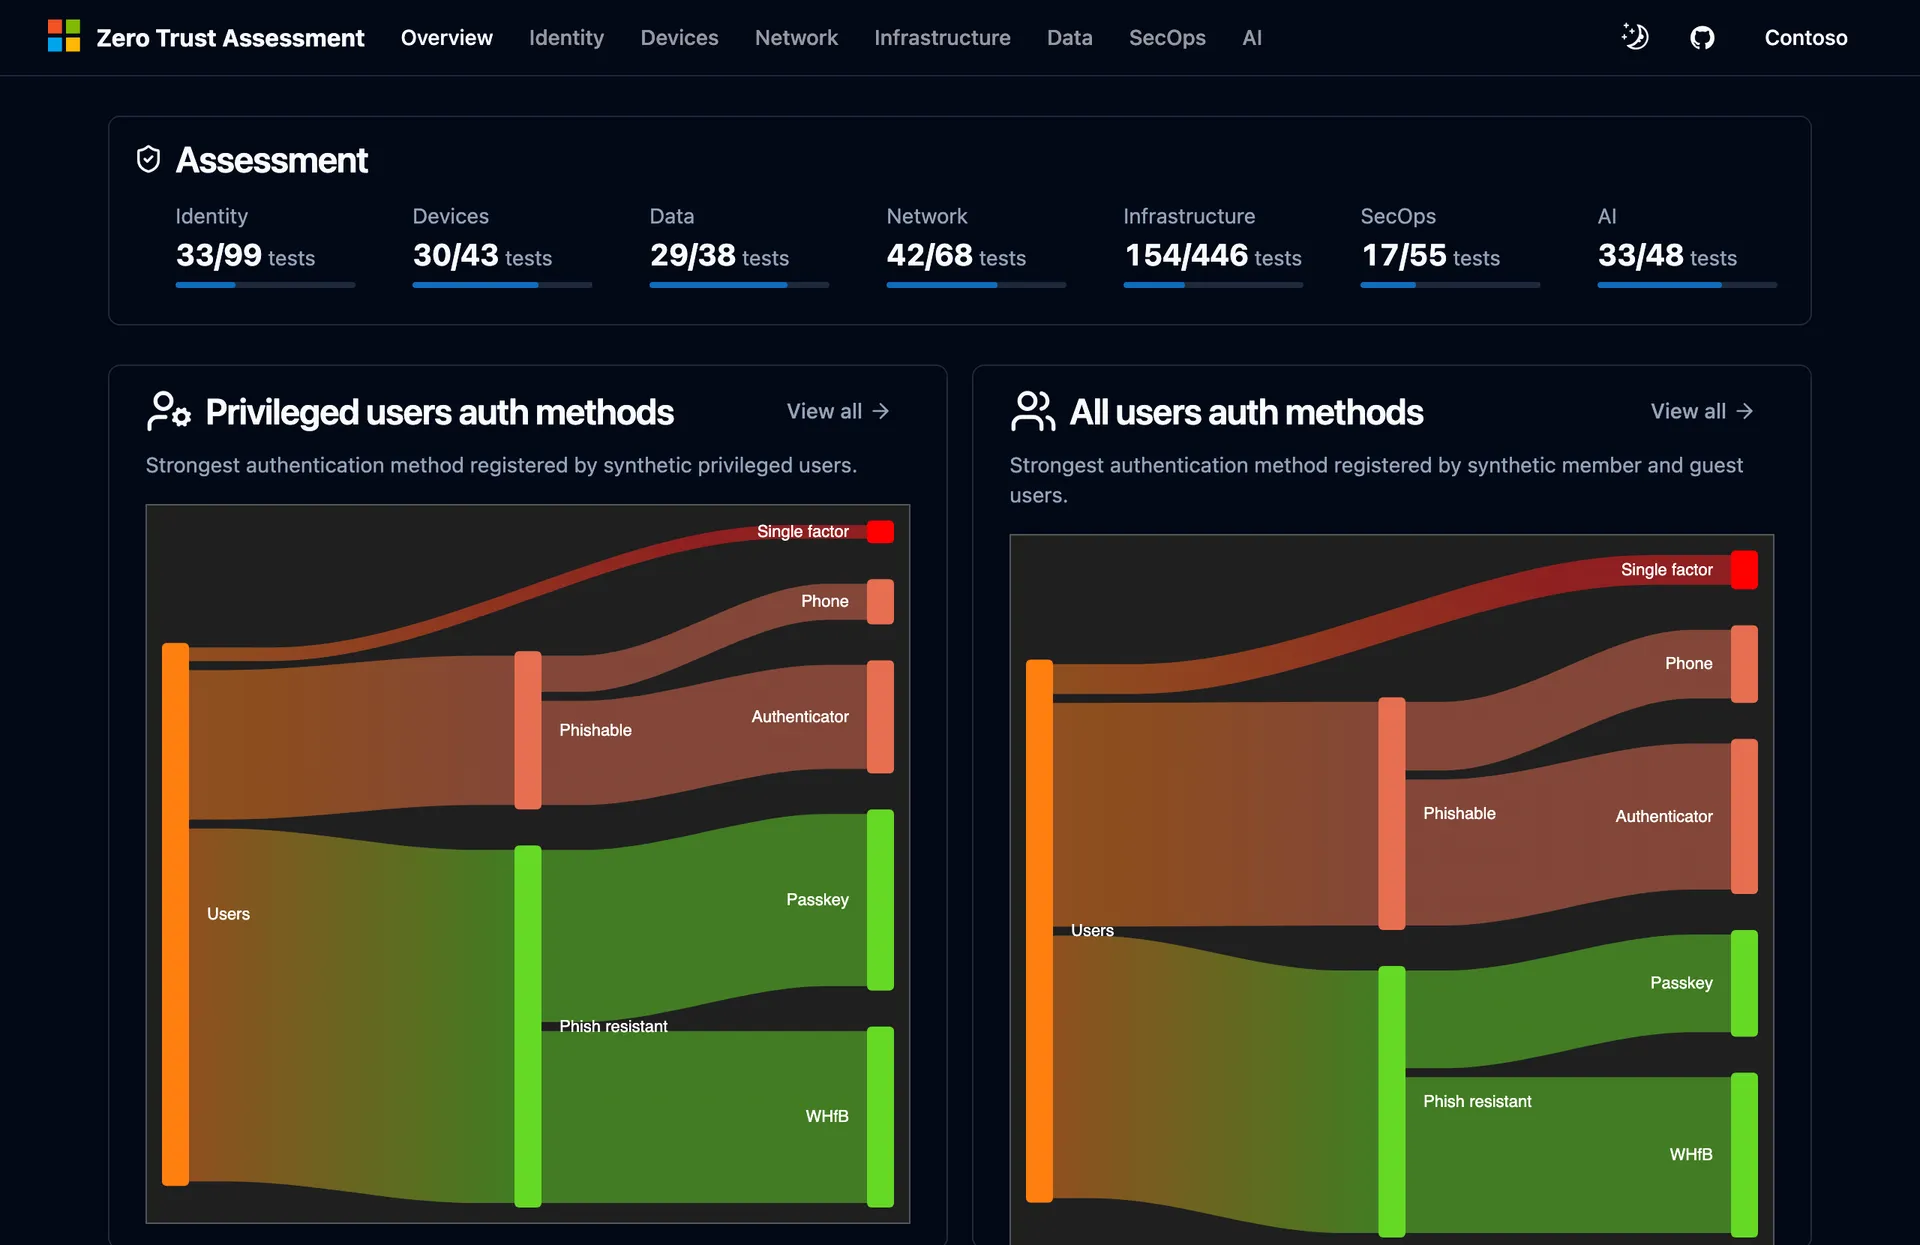
Zero Trust Assessment
Microsoft's assessment, in your Maester report.
The pack ships with Maester. One command runs both, and the plan turns the results into work.
Invoke-Maester -Pack ZTA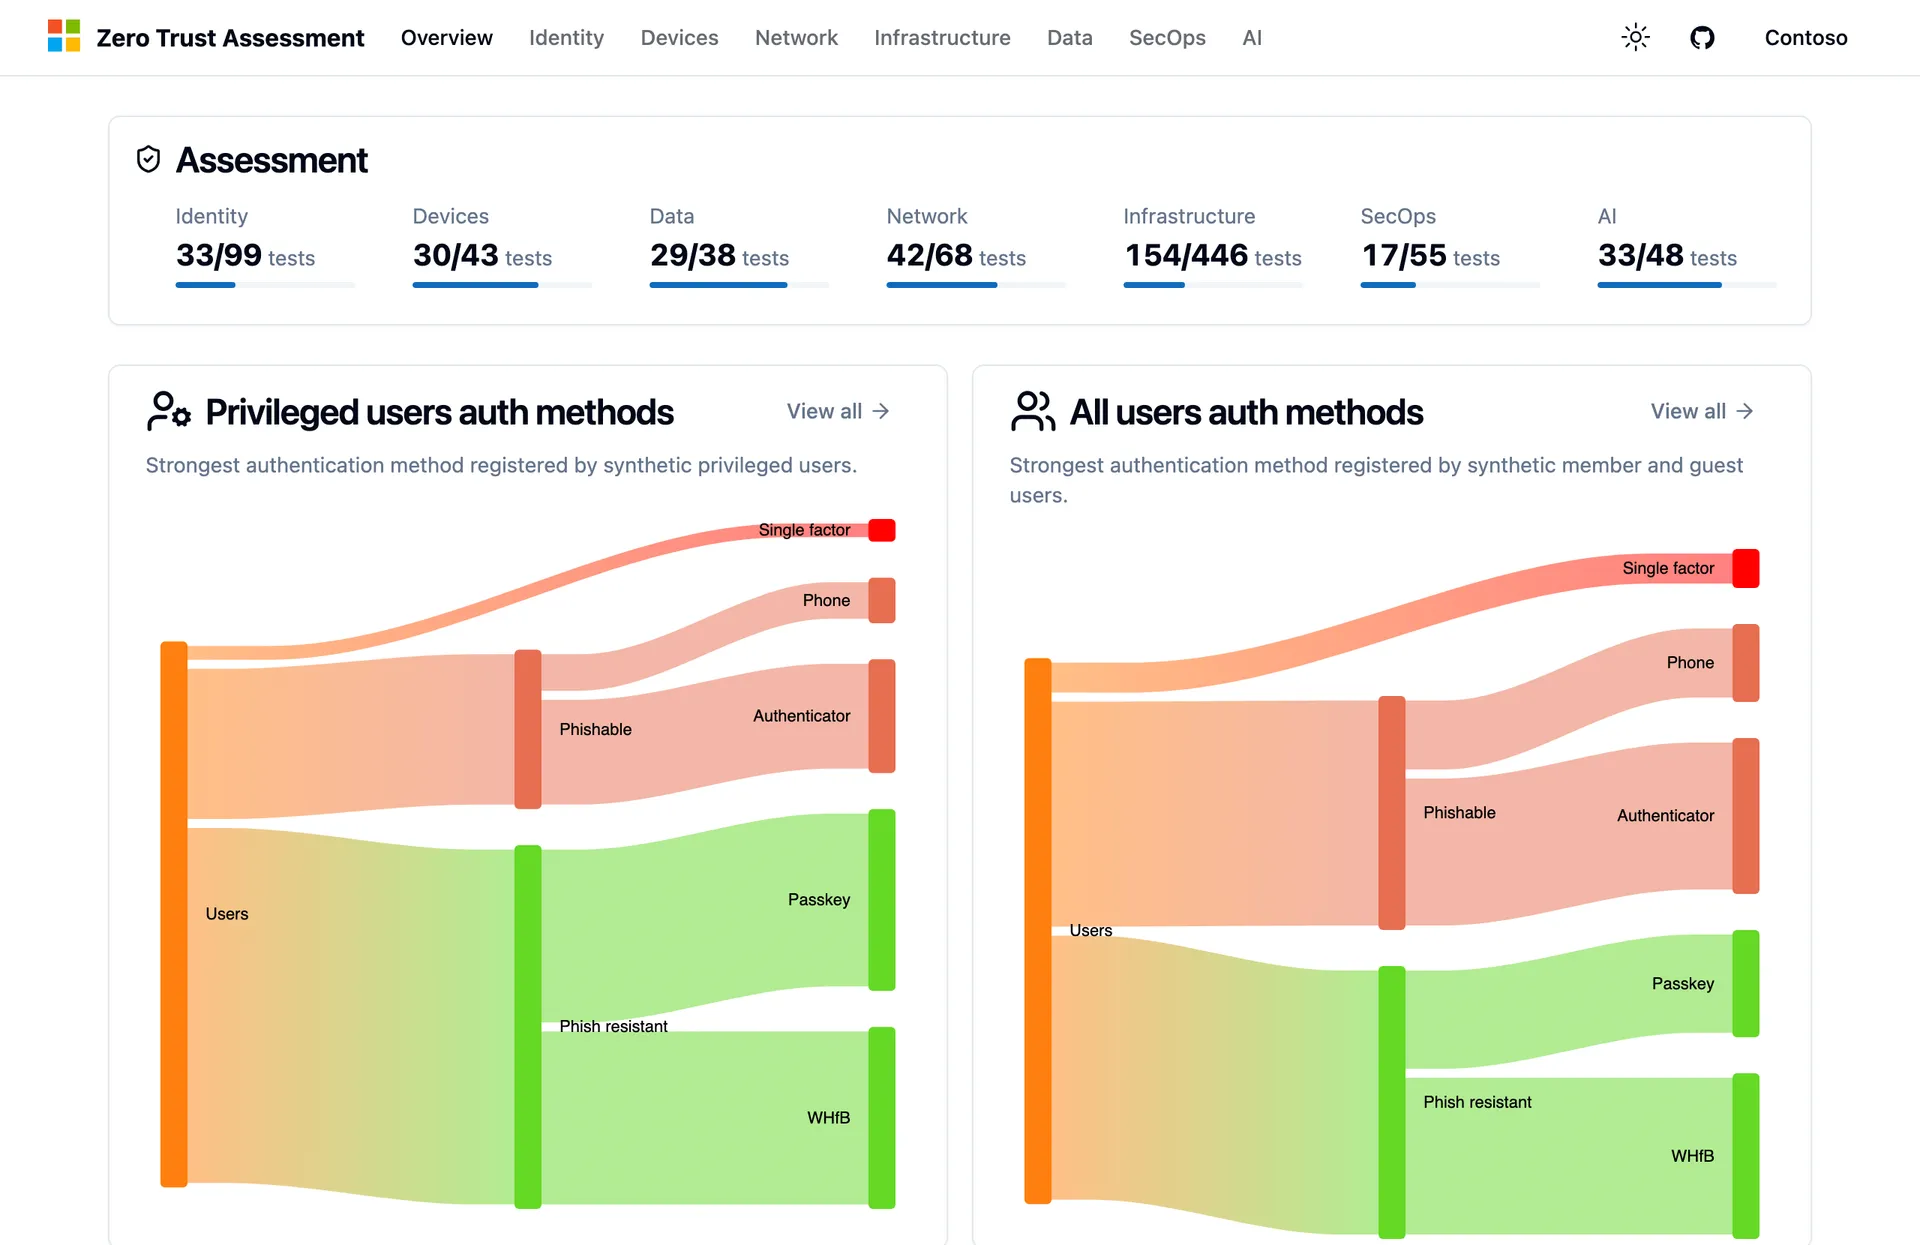
Security config as code
Define your security config as code.
Write each policy as a Maester test: one PowerShell function that says how your tenant must be set up. Maester runs it with everything else and puts it in the same report.
- Policies in a repository. Every rule your tenant must follow, versioned and reviewed like any other code.
- Regression tests for your tenant. Run them after every change, by hand, from a pipeline or after Terraform, and see at once what a change broke.
- Guardrails for AI agents. When an agent changes your configuration, it runs your Maester tests to check its own work, and keeps running them to watch for drift.
function Test-CT1001 {
    [MaesterTest(Id = 'CT.1001',
        Title = 'Our licensing groups are not empty')]
    param()
    # The groups that assign licences in this tenant
    foreach ($name in 'LIC-M365-E5', 'LIC-Copilot', 'LIC-Intune-Suite') {
        $group = Invoke-MtGraphRequest 'groups' -Filter "displayName eq '$name'"
        if (-not $group) { return $false }
        $count = Invoke-MtGraphRequest "groups/$($group.id)/transitiveMembers/`$count"
        if ($count -eq 0) { return $false }
    }
    $true
}
04New in 3.0
Maester 3.0. Rebuilt to run faster and say more.
A test engine of its own, checks that ship in the module, and a reason for every skip.
05Community
Built in the open by 77+ contributors.
Security practitioners, Microsoft MVPs and Microsoft engineers write the checks.




Maester or Maester Cloud
Same checks. You choose who runs them.
Maester is free and you run it yourself. Maester Cloud runs it for you, securely in Azure, and keeps every run.
Sponsors
Thank you, sponsors.
Maester is free because of the people and companies who pay for it. There are three ways to support it.